Pro · Login security
WP Security Ninja
Stop bots from hammering your login page
Limit failed logins, hide the default login URL, and add 2FA so stolen passwords and credential stuffing are much harder to abuse.
- ✓ Brute-force limits
- ✓ Rename login
- ✓ 2FA ready
Limit failed login attempts
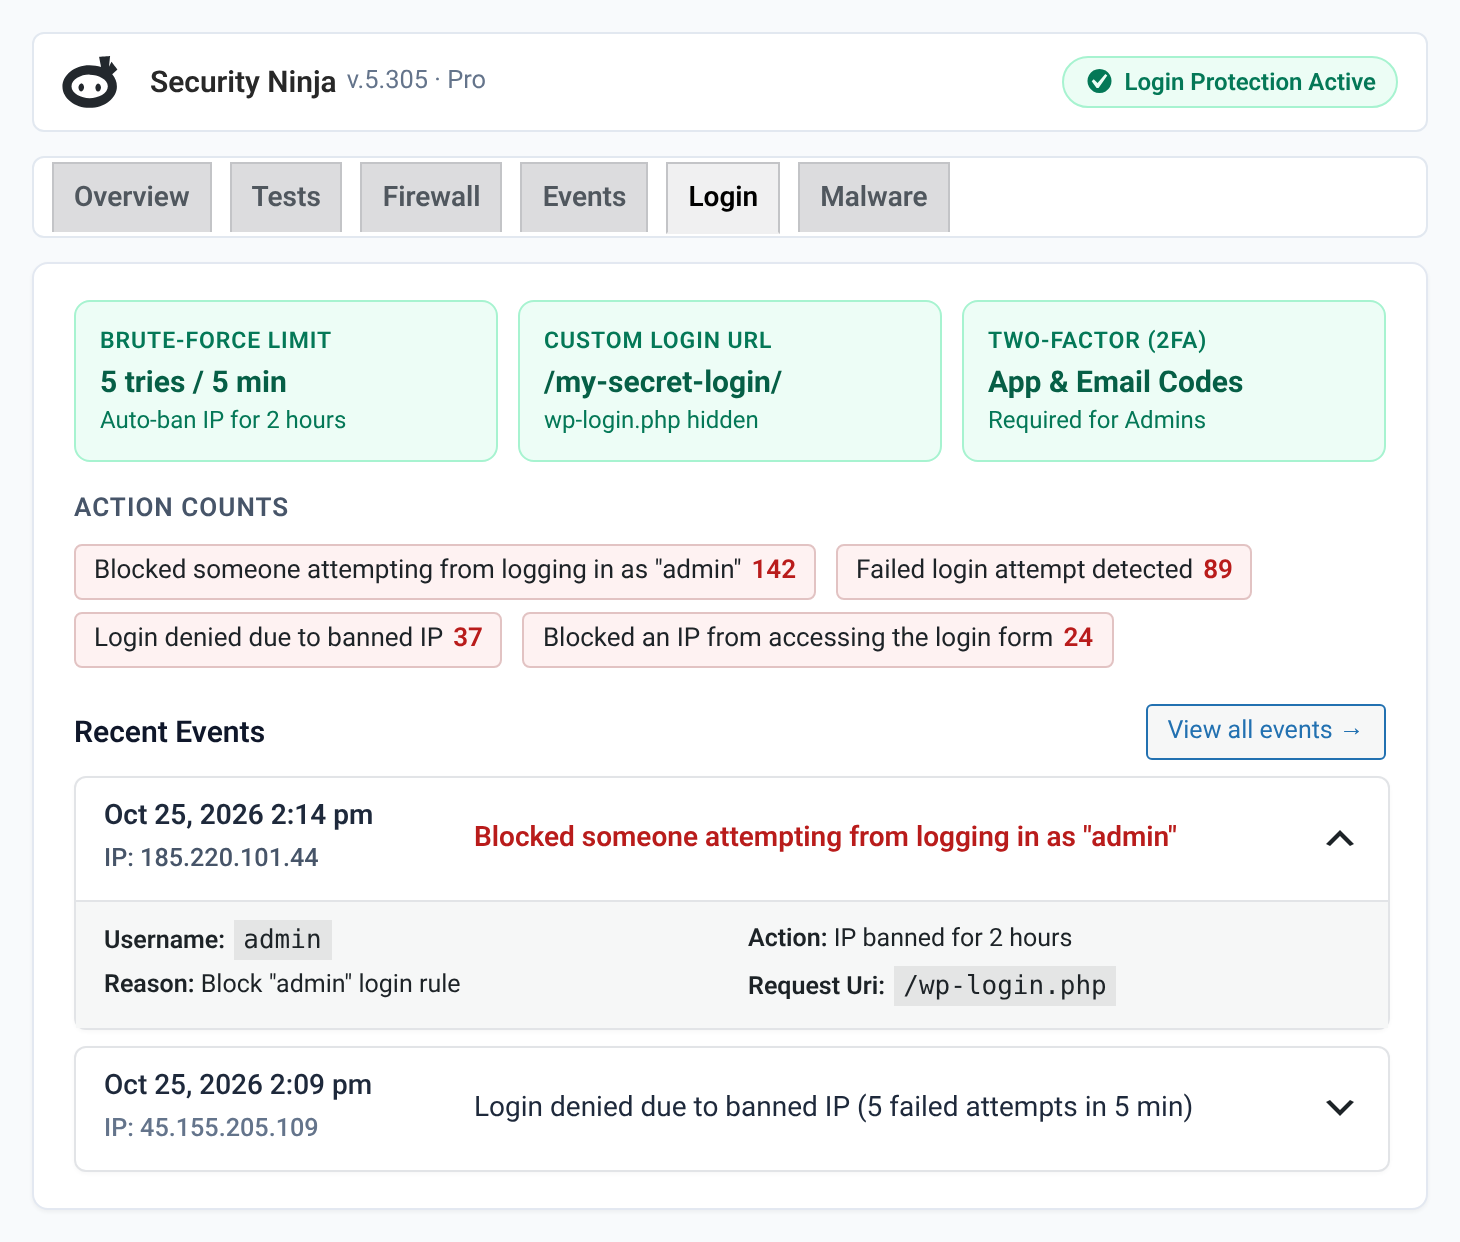
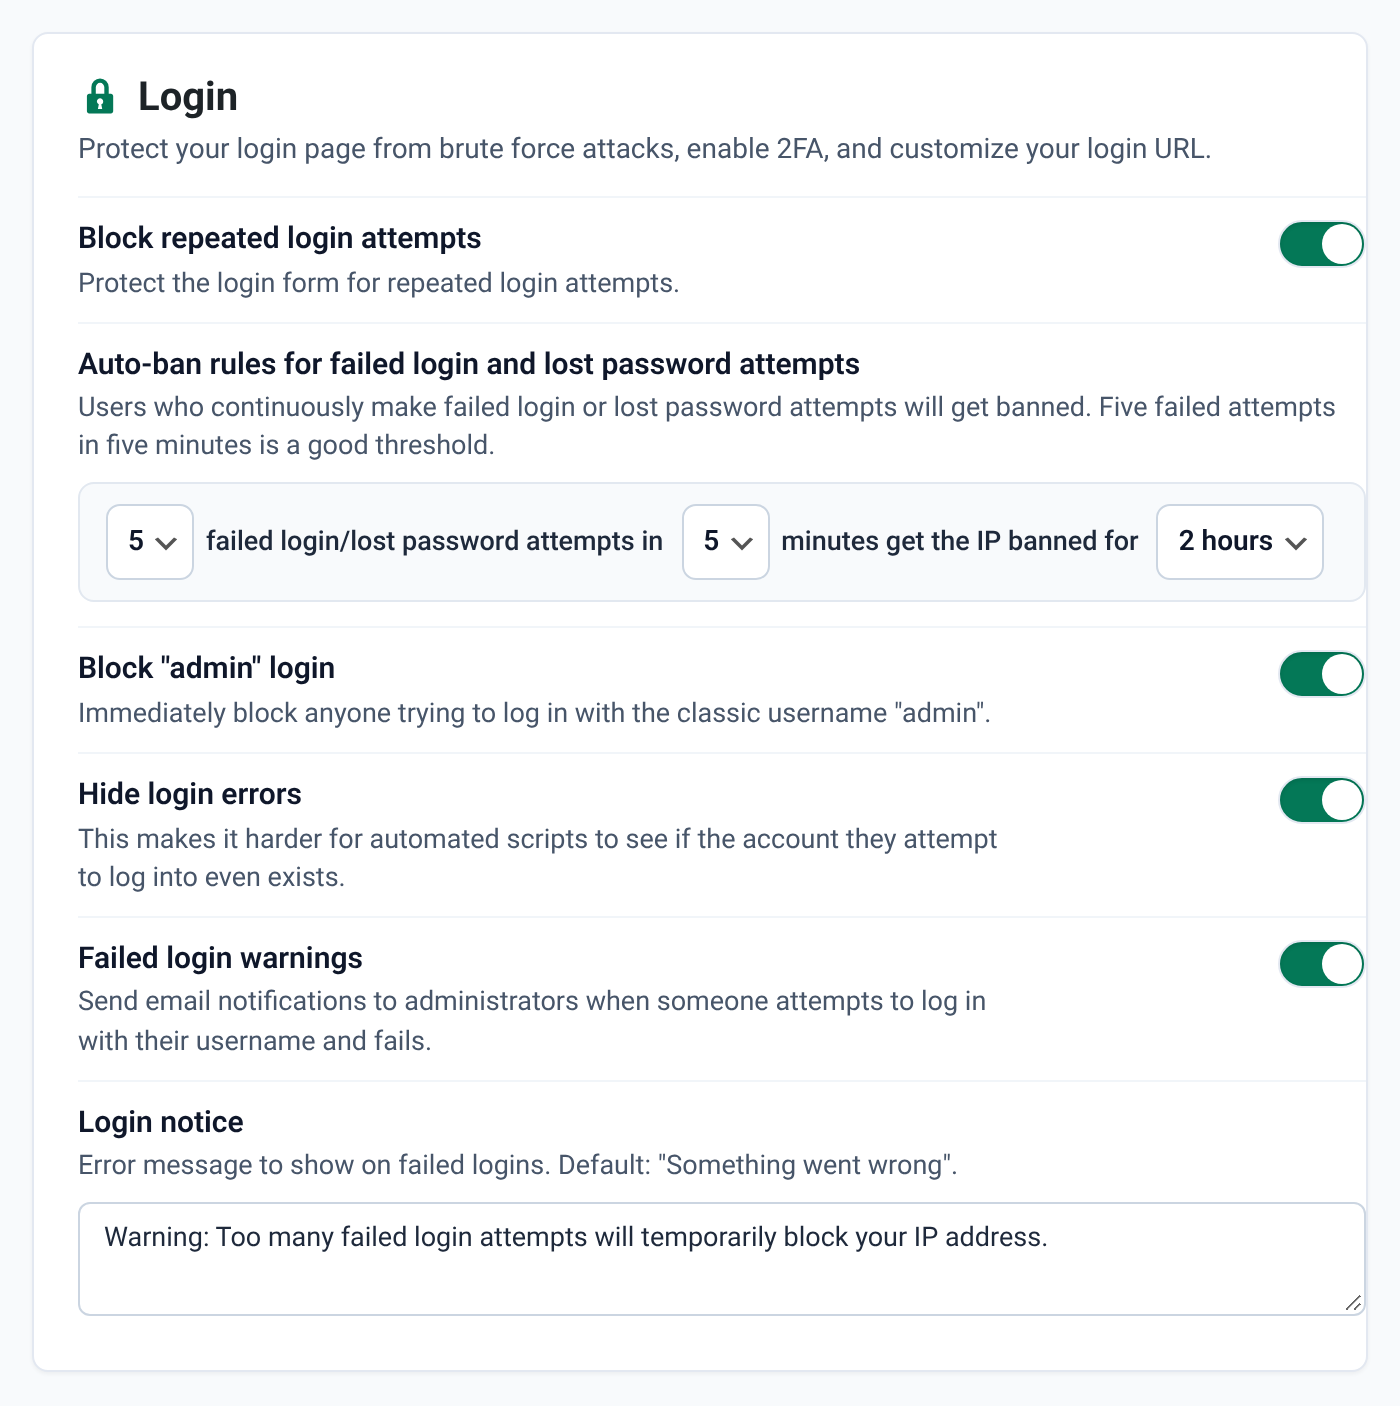
Attackers try thousands of passwords per minute. Pro login protection slows them down automatically with configurable auto-ban rules and clear messaging for blocked attempts.
- ✓ Auto-ban IPs after repeated failed logins or password resets (e.g. 5 attempts in 5 minutes)
- ✓ Instantly block bots trying to sign in with the classic 'admin' username
- ✓ Hide generic login errors to stop username enumeration and customize lockout notices
Rename the login URL
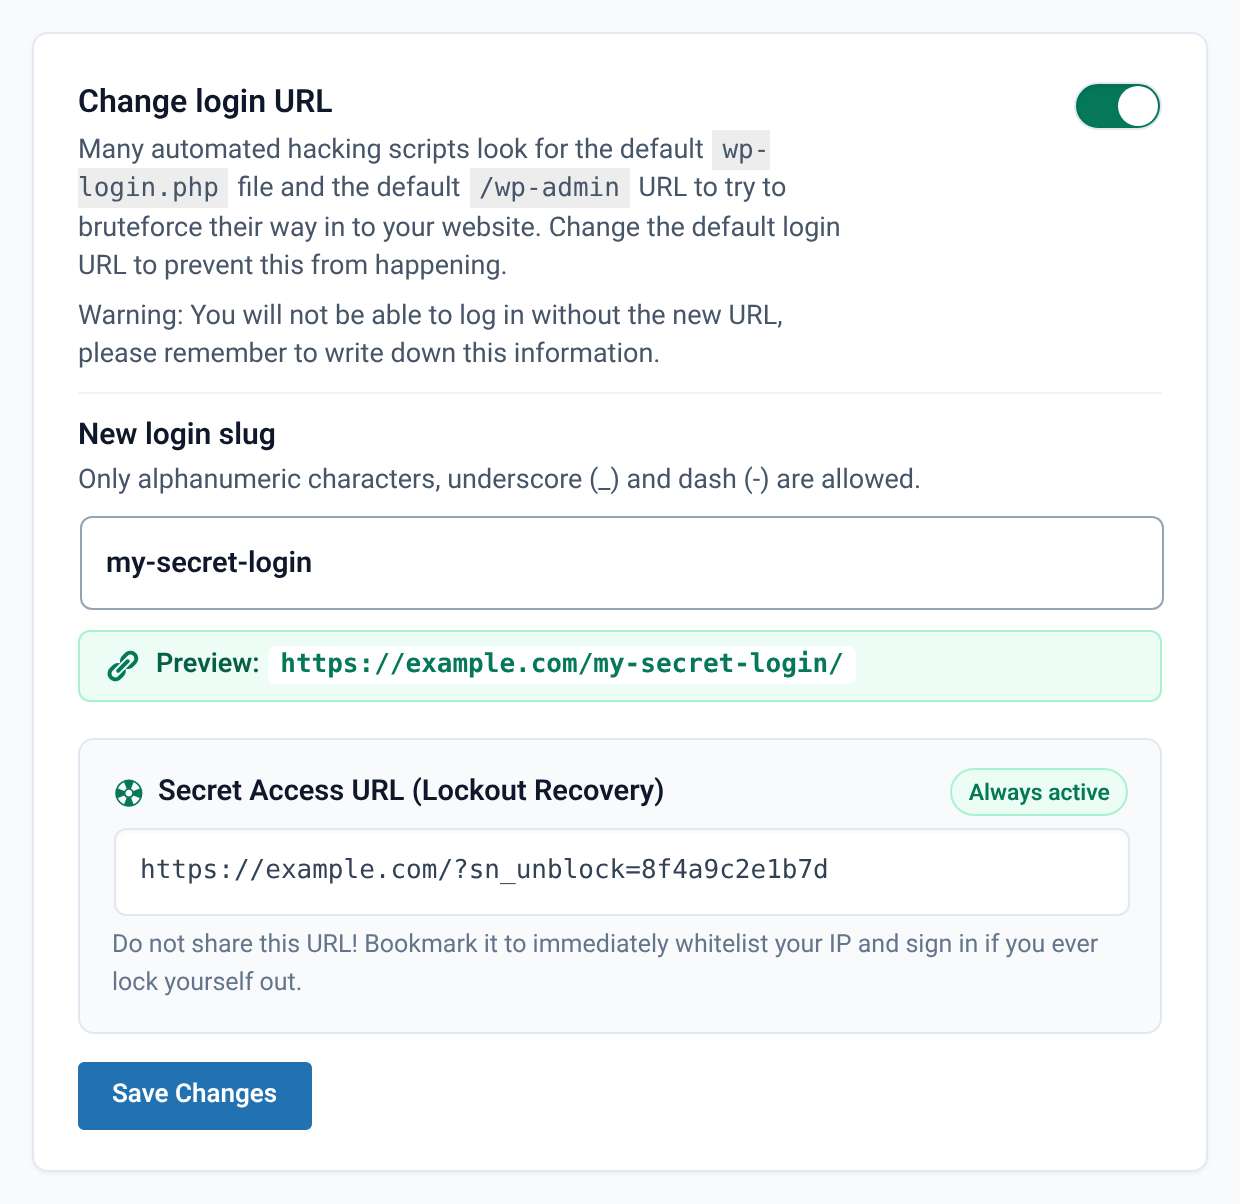
Every bot script targets /wp-login.php first. A custom login slug means automated scanners stop finding the door, while you and your team still sign in normally.
- ✓ Replace /wp-login.php with your own custom login slug in seconds
- ✓ Live URL preview shows the exact sign-in link your team will use
- ✓ Built-in Secret Access URL lets you whitelist your IP and recover access if you ever lock yourself out
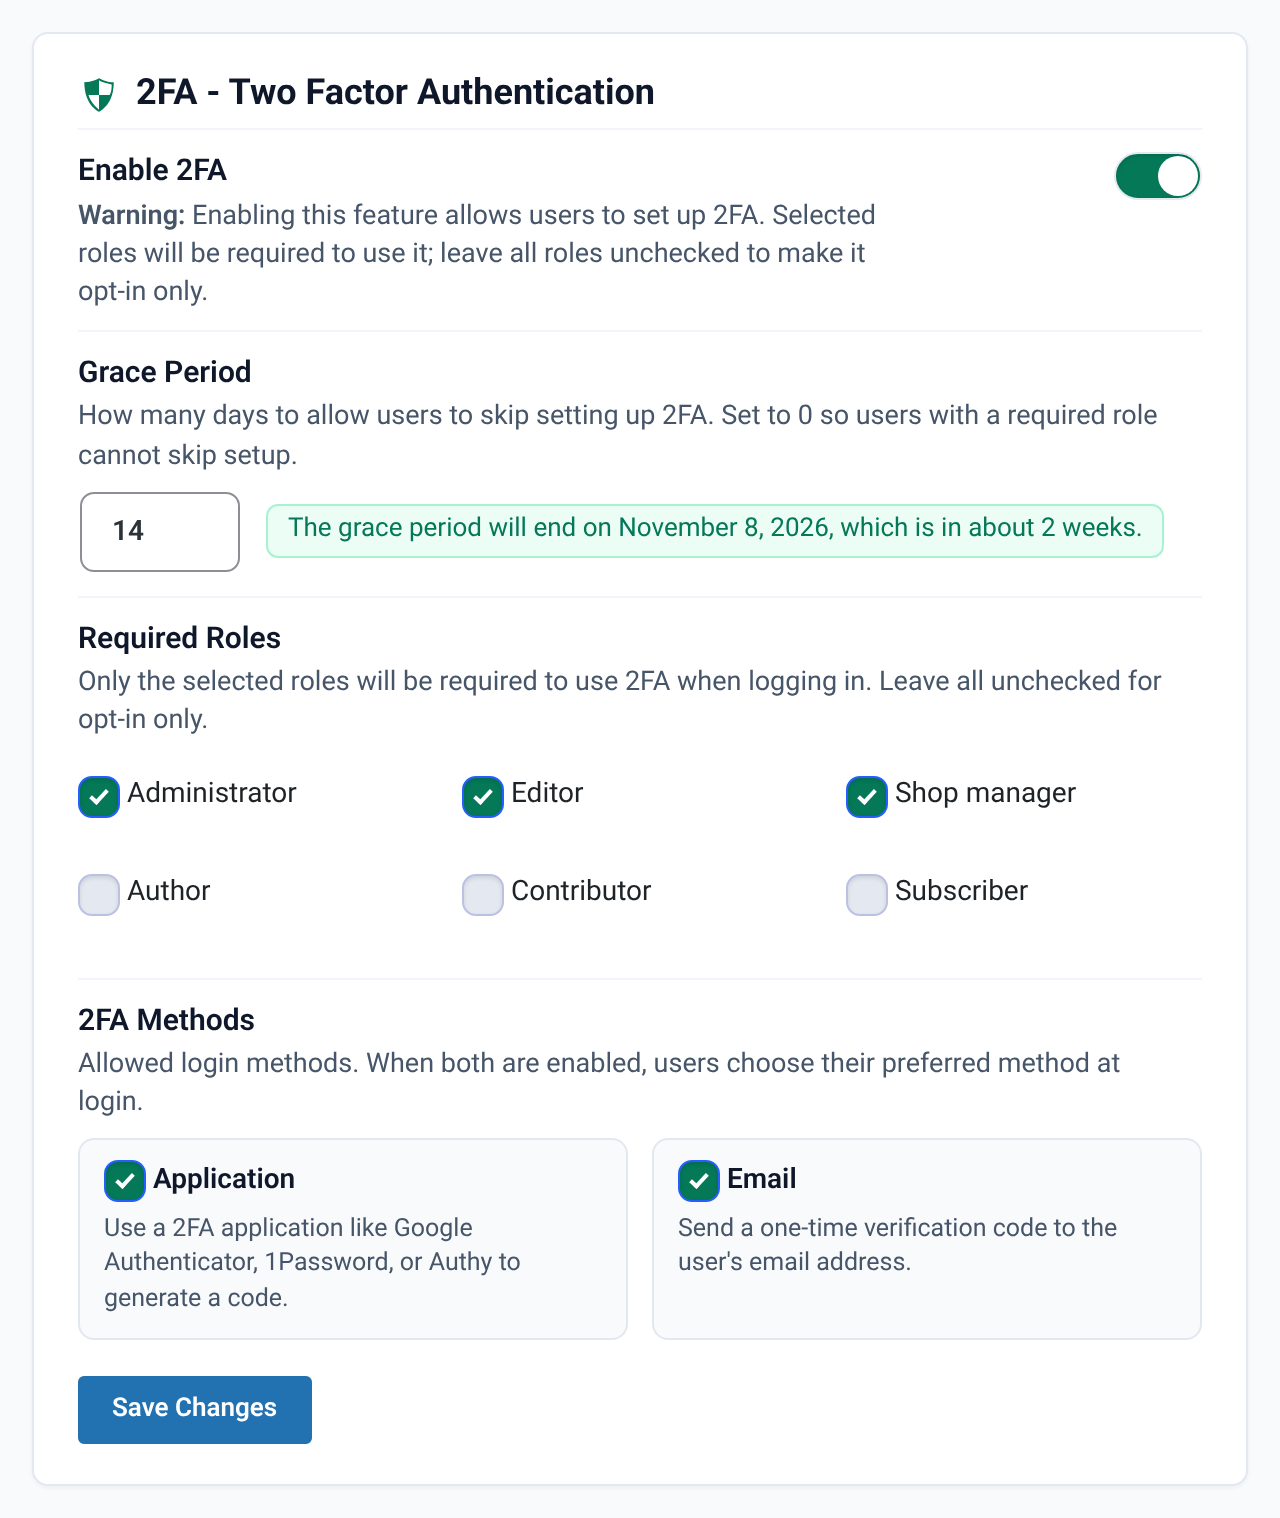
Add two-factor authentication
Even a strong password can leak. Require authenticator apps or email verification codes for the roles that matter, with opt-in and grace period options.
- ✓ Require 2FA for specific roles (Administrator, Editor, Shop manager) or leave it opt-in
- ✓ Let users verify with an Authenticator app (Google Authenticator, 1Password, Authy) or one-time email codes
- ✓ Configurable grace period (e.g. 14 days) so your team can enroll without sudden lockouts
Customer reviews
4.9 / 5 from 263 reviews
Excellent Plugin
“Security Ninja has everything and more of what you’d want in a security plugin. Some examples are the firewall, limited login attempts, malware scanner, logs, and alerts.”
So Glad to Find This
“WP Security Ninja Review I've been using WP Security Ninja for several weeks now, and I must say, it has exceeded all my expectations.”
Works well as a base security plugin
“WP Security Ninja stands out with a balanced and clear mix of features. It works well as an all-in-one solution but remains simple enough to combine with tools like Patchstack with…”
Amazingly user-friendly security plugin
“Thank you, Security Ninja! Your plugin is easy to use, provides clear reports of activity, and includes built-in tools that make security a lightweight task.”
Frequently asked questions
Is login protection free? +
Failed-login limits, rename login, and 2FA are Pro features. Free still logs login successes and failures in the basic Events Logger and includes over 50 security tests.
Will rename login break my site? +
No, it only changes the address where you and your team sign in. Use the live preview, bookmark your new URL, and keep your Secret Access URL saved for instant lockout recovery.
What if I lock myself out or forget my custom login URL? +
Security Ninja Pro generates a private Secret Access URL for your site. Bookmarking and visiting that link immediately whitelists your IP address and restores access so you never have to disable the plugin via FTP.
Harden WordPress logins with Pro
Get login limits, rename login, and 2FA together with Cloud Firewall and malware scanning.
Get Pro