Flags updates waiting, stale plugins, and inactive themes or plugins you forgot about.
Learn moreFree · Detect & harden
WP Security Ninja
See what's risky on your WordPress site in one run
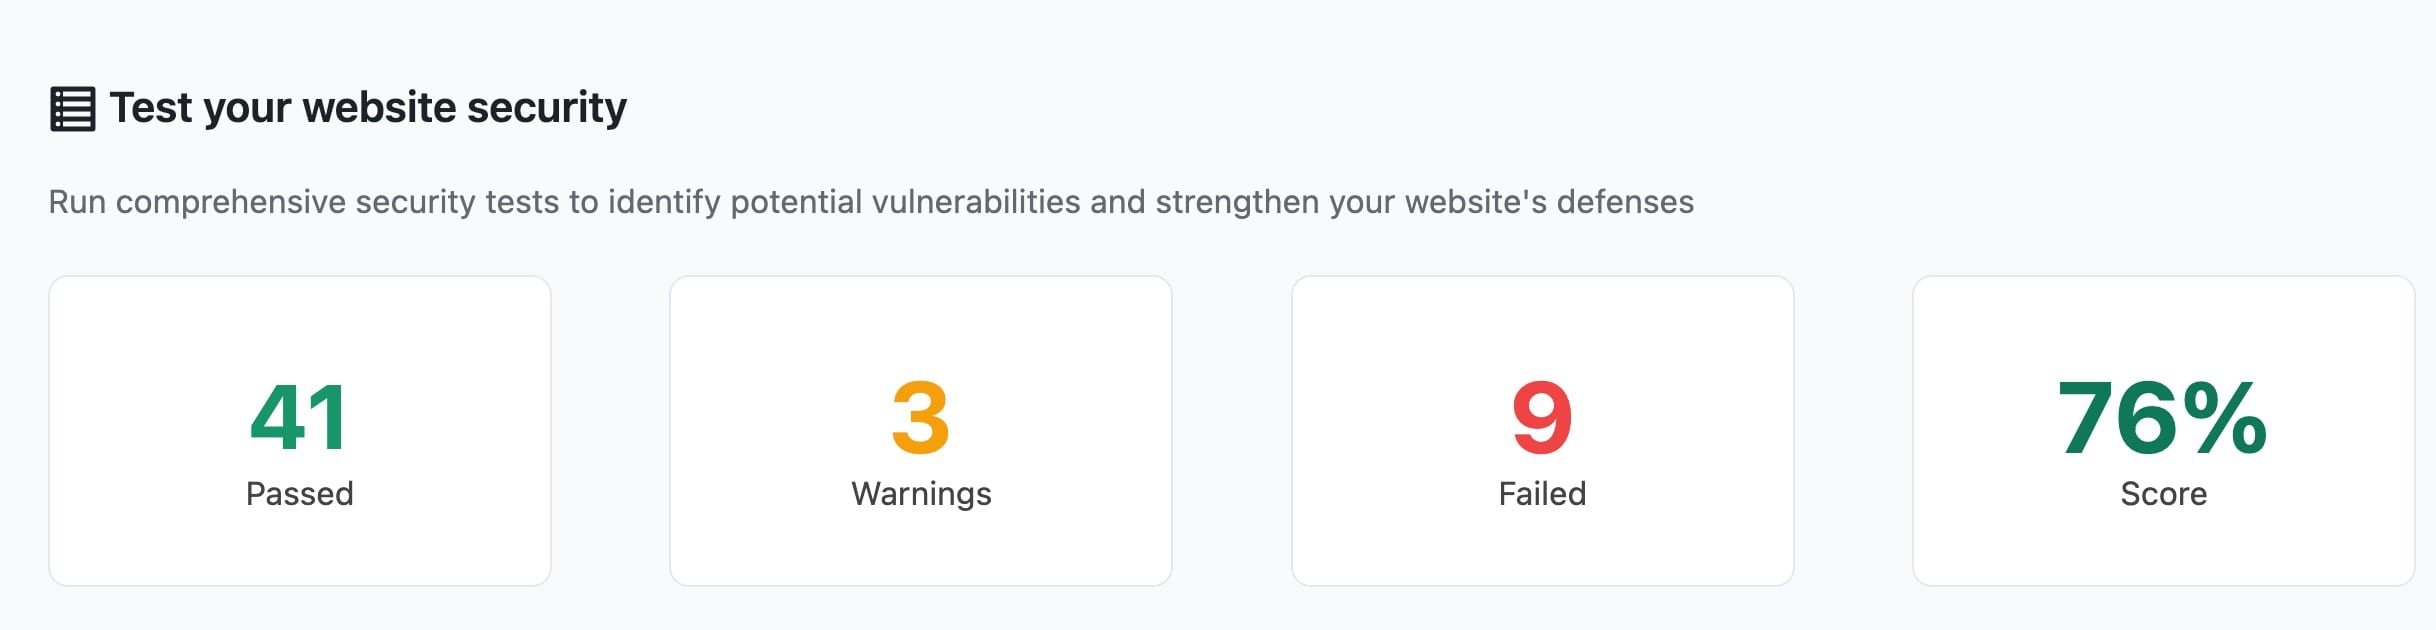
Security Tests check 50+ common hardening gaps, from outdated plugins to readme.html version disclosure and exposed config files. You get a weighted score, clear pass and fail counts, and fix guidance on every result.
- ✓ 50+ hardening checks
- ✓ Weighted security score
- ✓ Fix steps on every test
How it works
A checklist with answers, not just red flags
Run the tests once and you get a prioritized view of what needs attention, plus plain-language guidance for each finding.
-
Run the tests
One click from Security Ninja. The Install Wizard can start them in the background on a fresh install.
-
See your score
A weighted percentage plus Passed, Warning, and Failed counts. Filter the list to focus on what matters.
-
Open Details
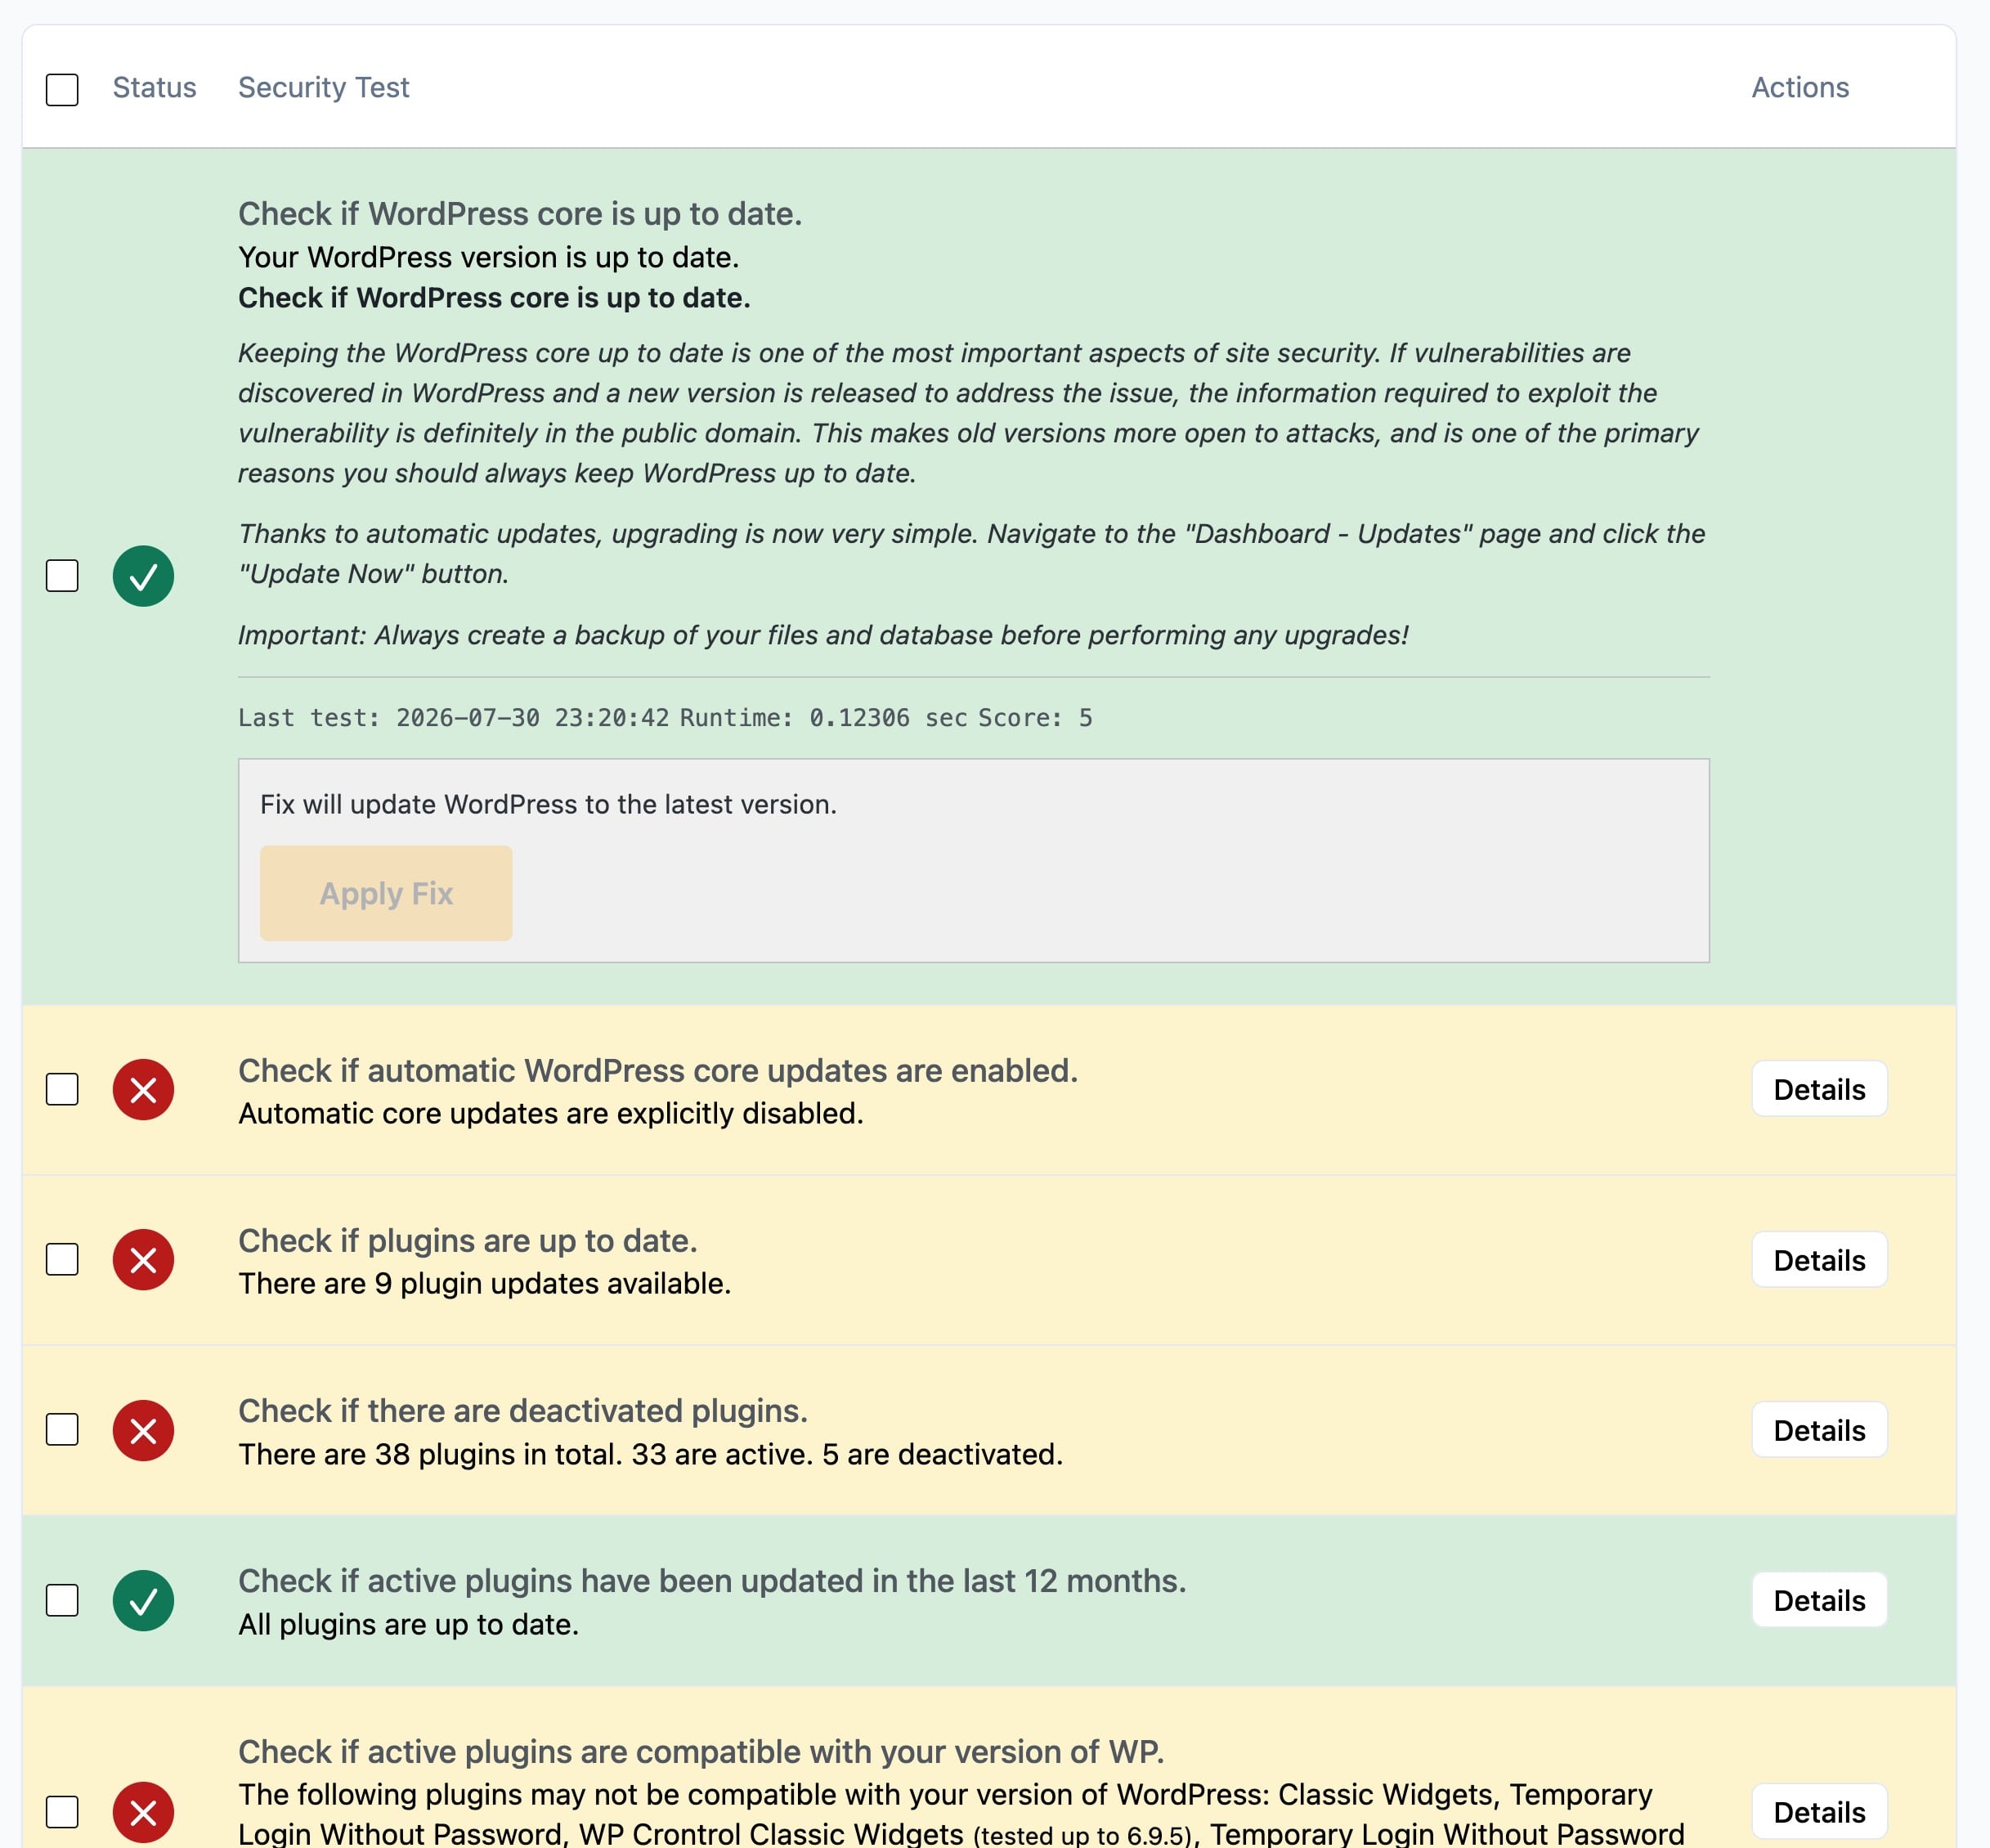
Every result explains the risk, why it matters on WordPress, and what to change. Most fixes are manual steps you can follow today.
Things tests catch that are easy to miss
These show up on real sites every week. Tests flag them so you can decide what to fix first.
- ✓ A user still named admin with full privileges
- ✓ Anyone can register left enabled on a site that does not need it
- ✓ Public readme.html version disclosure in the WordPress root
- ✓ Full WordPress version visible in page source
- ✓ A wp-config.php backup file sitting in the web root
- ✓ Missing security headers you can add without breaking the site
What gets checked
50+ tests across the things attackers actually probe
Not a generic scan. These checks target real WordPress misconfigurations that show up on hacked and neglected sites.
Software you run
Outdated code is the easiest way in.
Spots active plugins that may not match your WordPress version.
Learn moreSecrets and config
Small wp-config mistakes cause big problems.
wp-config.php permissions and location
Checks file rights and whether the config file sits where it should.
Finds WP_DEBUG left on, debug.log in the open, and encryption keys that should be rotated.
Learn moreDatabase prefix and password strength
Warns about default wp_ prefixes and weak database credentials.
What attackers can learn
Information disclosure helps targeted attacks.
Checks whether WordPress readme.html is public and leaking your core version. Fix guide included.
Learn moreVersion tags in page source tell attackers exactly which exploits to try.
Learn moreBrowsable uploads and backup files
Finds wp-config.php.bak, .sql dumps, phpinfo.php, and other files that should not be public.
Catches anyone-can-register and a user still named admin.
Learn moreServer and headers
Hosting settings and HTTP headers matter too.
Checks PHP version, expose_php, display_errors, and related server settings.
Learn moreSecurity headers
HSTS, CSP, X-Frame-Options, Referrer-Policy, and Permissions-Policy when your host allows them.
Username enumeration, failed-login error leakage, and user ID 1 checks.
Learn moreYour security score is not a mystery number
The score weighs each test by impact, so a failed core update counts more than a minor header warning. Passed, Warning, and Failed counts give you a quick read before you dig into Details.
- ✓ Weighted percentage reflects real risk, not just pass/fail tallies
- ✓ Filter by Failed, Warning, Passed, or Untested
- ✓ Re-run after fixes to track improvements
Every failed test comes with a plan
Click Details on any result and you get context: what the test checked, why it matters, and steps to fix it. Warnings often mean review this, not panic. Some items depend on your host, and the guidance says so.
- ✓ Plain-language explanations, not error codes
- ✓ Manual fix steps included free on every test
- ✓ Docs for common failures when you need more depth
Pro when you want fixes faster
The full test suite is free on Free and Pro. Pro adds one-click Auto Fixer on many failing tests, a Fixes settings page for headers and hardening toggles, and scheduled re-runs so you catch regressions.
- ✓ Auto Fixer applies safe changes without editing files by hand
- ✓ Fixes page for security headers, XML-RPC, editors, and more
- ✓ Schedule test runs with Pro Scheduled Scanner
Free vs Pro
Same tests on Free and Pro. Pro adds speed.
Every install gets the full audit, scoring, and manual fix guidance. Upgrade when you want one-click fixes and scheduled re-runs.
Forever free
Free
The complete security test suite, included with the WordPress.org plugin.
- All 50+ security tests
- Weighted security score
- Details and manual fix steps on every test
- AI Security Advisor context on supported WordPress versions
Save time fixing
Pro
Everything in Free, plus tools that turn results into actions faster.
- Everything in Free
- One-click Auto Fixer on many failing tests
- Fixes settings page for headers and hardening toggles
- Scheduled test runs with Scheduled Scanner
Customer reviews
4.9 / 5 from 261 reviews
Very helpful
“Security Ninja is part of my arsenal that I offer to my clients. It helps make sure their websites are security and scans them for malware.”
No WordPress plugin should be your entire security stack, but this one is a solid choice to be a key part of it.
“I've been a web host and sysadmin for 15 years. I'm skeptical when it comes to security tools, and many of them out there are either bogged down bloatware, don't do enough, or try…”
Fast security audit with one-click fixes, but use judgment
“I installed WP Security Ninja on my own WordPress website, ran a scan, and fixed several real issues in under an hour.”
Great offering
“My Wordpress site had recently been compromised even when I had a scanning plugin that was supposed to detect malware.”
Frequently asked questions
What is WordPress readme.html version disclosure? +
WordPress ships a readme.html file in the site root. When it stays public, anyone can open it and often learn which WordPress version you run. That is version disclosure. Attackers use it to pick known exploits for that release. Security Tests checks whether readme.html is reachable over HTTP.
Is exposing readme.html dangerous? +
It is not a remote code execution bug by itself. It still helps targeted attacks by confirming you run WordPress and which core version is present. Removing or blocking readme.html is a standard hardening step alongside hiding version tags in page source.
How do I remove or block WordPress readme.html? +
Delete readme.html from the WordPress root (same folder as wp-config.php) via FTP or your host file manager, or block HTTP access with server rules. On Pro, the Remove Unwanted Files fix can clear readme.html and similar leftover files in one step. Full steps: secure or remove readme.html in the Security Tests docs.
Are all security tests free? +
Yes. Free and Pro run the same 50+ tests with the same scoring and Details guidance. Pro adds one-click Auto Fixer, the Fixes settings page, and scheduled re-runs.
Do I need 100% to be safe? +
No. A perfect score is rare and not always realistic. Warnings often mean review this, not drop everything. Read Details for each result and fix high-impact failures first. See our guide on security issues were found.
Do tests fix issues automatically? +
Free includes manual fix steps on every test. Pro can apply many fixes with one click through Auto Fixer. Some changes still need a host, developer, or deliberate choice on your part.
What do security tests not cover? +
Tests check configuration and hardening, not live malware or incoming attack traffic. For file-level threats use the Pro malware scanner. For blocking bad visitors use Cloud Firewall and login protection.
How often should I re-run tests? +
After plugin updates, config changes, or when you inherit a site. Pro can schedule recurring test runs with Scheduled Scanner and include results in email reports.
Where do I read about a specific failure? +
Click Details in the plugin, or browse the Security Tests docs hub. We have individual articles for common failures like readme.html version disclosure, open registration, and default admin users.
Install free. Run your first audit today.
Download from WordPress.org, run the tests, read Details on anything that fails, and upgrade to Pro when you want one-click fixes.
Try Free