Biblioteca de seguridad WordPress
Blog
140 artículos prácticos sobre malware, protección de acceso, endurecimiento y cómo mantener seguros los sitios WordPress.
Los artículos están en inglés. Los temas y esta página están en español para orientarte.
Empieza aquí
Guías pilar que la mayoría de dueños de sitios necesitan primero (EN).
- WordPress Security for Beginners 2026: Easy Protection Guide EN WordPress security for beginners: simple steps for updates, logins, plugins, backups, scanning, and what to do if something looks wrong.
- WordPress Login Security Guide 2026 EN How to secure a WordPress login page: strong passwords, 2FA, failed-login limits, fewer admins, optional login URL rename, and monitoring that catches bots early.
- WordPress Security Checklist 2026: Complete Site Protection Guide EN A printable WordPress security checklist: HTTPS, updates, passwords/2FA, backups, WAF/scans, least privilege, admin hardening, remove unused, and monitoring.
- WordPress firewall plugins EN A WordPress firewall plugin filters bad HTTP before it hits wp-admin. Plugin vs cloud WAF, what it actually blocks, and how to pick one without stacking tools.
- WordPress security scanner comparison EN What a WordPress security scanner actually does: vulnerability checks, malware scans, and core integrity. How to pick one you will run, including Security Ninja.
- Free vs premium WordPress security plugins EN Free vs premium WordPress security plugins: what free usually covers, when Pro is worth it, and how Security Ninja Free and Pro map to real protection.
- WordPress security hardening EN Practical WordPress hardening: updates, wp-config, permissions, logins, SSL, plugins, XML-RPC, .htaccess, firewall, scans, and backups in a sensible order.
- Best WordPress security plugins EN Best WordPress security plugins by job: Security Ninja, Wordfence, Sucuri, MalCare, Patchstack, and Solid Security. What each is strong at, and how we choose.
- WordPress security guide EN A practical WordPress security hub: ordered paths for beginners, agencies, stores, and incident response, plus links to checklists, hardening, login, firewall, and scanners.
- WordPress malware removal EN How to remove WordPress malware: contain the infection, clean or restore, rescan, rotate access, and close the hole so it does not come back.
- WooCommerce security EN How to secure a WooCommerce store: updates, strong logins, checkout rate limits, malware scanning, backups, and monitoring. No fake PCI guarantees.
- 7 Signs a WordPress Site Is Hacked EN How to tell if a WordPress site is hacked: unknown admins, lockouts, redirects, spam, Search Console warnings. Several signs together, not one glitch.


Malware y limpieza
Detecta, elimina y limpia malware y compromisos en WordPress.
- WordPress core files were modified: what it means A core-file warning means a checksum mismatch, not an automatic hack. How to read the diff, when it is harmless, and when to restore or treat it as malware.
- When a security plugin is enough vs when to hire cleanup A plugin is the weekly stack you run yourself. Hired cleanup is humans for a live compromise or a written review. How to buy the right job, not a second dashboard.
- WordPress Malware Cleanup: DIY or Hire Help? After you confirm a WordPress hack: when to clean malware yourself, when to hire cleanup, what a good incident response includes, and how to avoid paying twice.
- Check if Your WordPress Site Is Hacked Check if a WordPress site is hacked with scans from wp-admin: vulnerabilities, security tests, core integrity, then a logged-out look at users and Search Console.
- WordPress security patterns we keep seeing (and simple fixes) Recurring WordPress security problems: postponed updates, messy access, no logs, untested backups, bot noise, and one-time security installs. Plus a simple baseline.

Artículos en inglés
Inicio de sesión y acceso
Protege wp-login, frena la fuerza bruta y endurece el acceso de administrador.
- How to enable 2FA on WordPress Enable two-factor authentication on WordPress: authenticator app or email codes, which roles must enroll, grace period, and how to recover a lost phone.
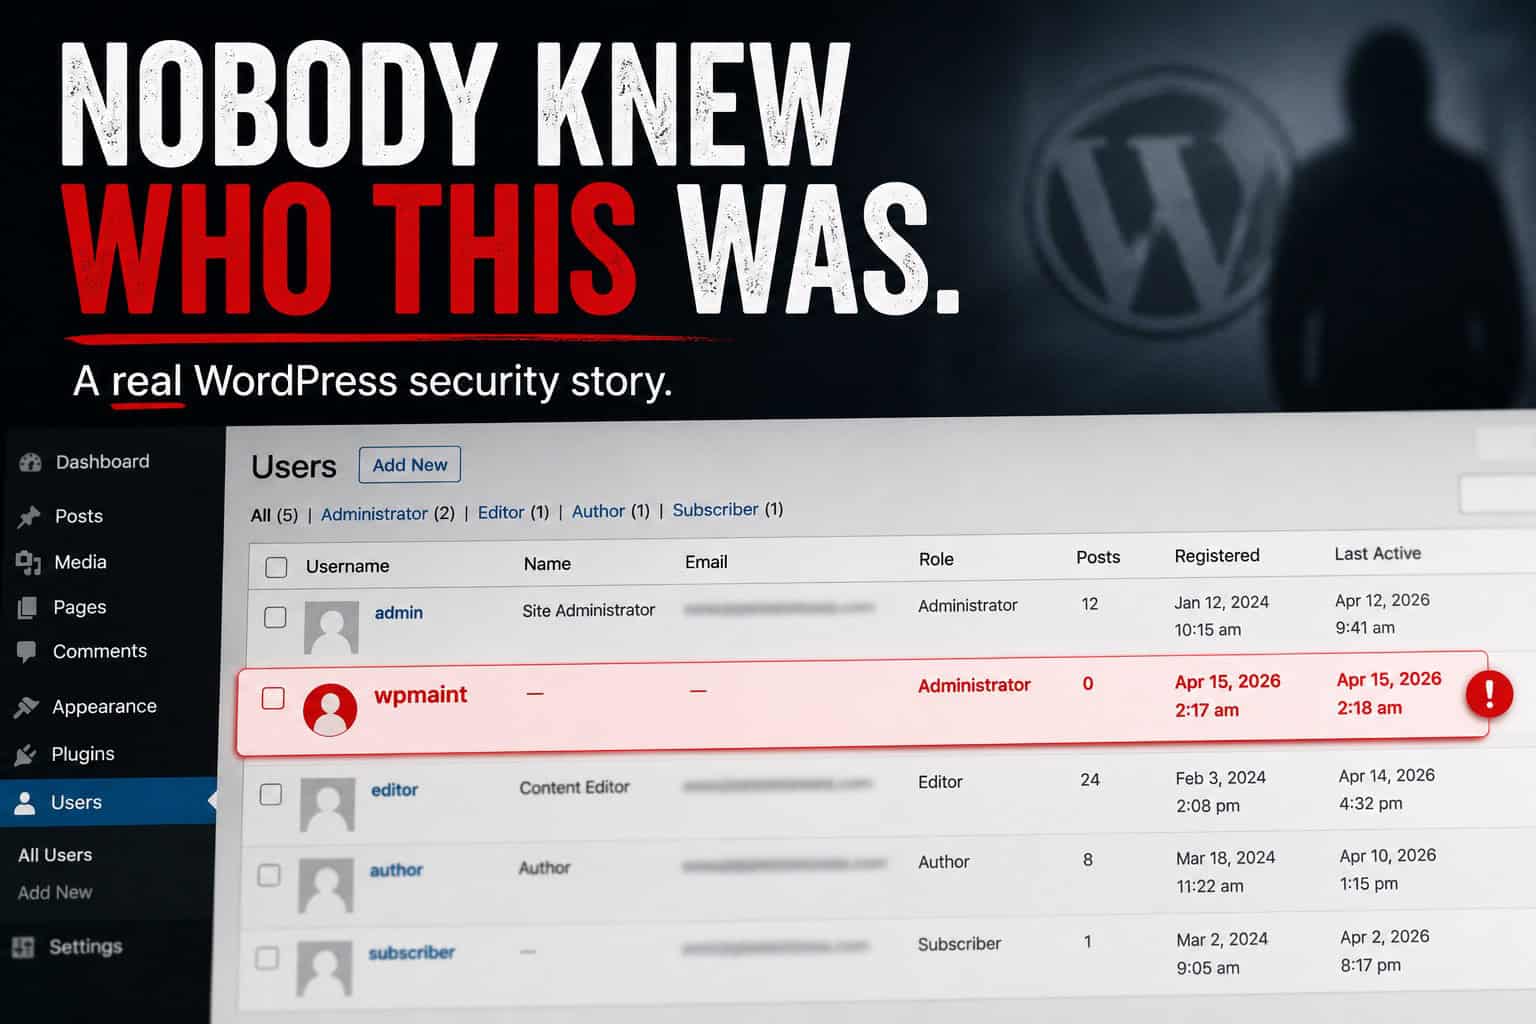
- An unknown WordPress admin: the calm response that keeps the incident short A client spotted an unrecognized administrator named wpmaint. How we contained access, checked plugins and themes, and left the site more disciplined than before.
- WordPress Login Security Guide 2026 How to secure a WordPress login page: strong passwords, 2FA, failed-login limits, fewer admins, optional login URL rename, and monitoring that catches bots early.
- WooCommerce Protected Categories: password and role gates Set up WooCommerce Protected Categories (Barn2) with passwords, roles, or users. Test add to cart, cache pitfalls, and store hardening that still matters.
- Password Management Tips for WordPress Sites Numbered password practices for WordPress: unique passwords, managers, team sharing, 2FA, recovery codes, and audits without duplicating the full login guide.
Artículos en inglés
Endurecimiento y listas de comprobación
Pasos prácticos de endurecimiento, auditorías y checklists que se mantienen.
- How to enable 2FA on WordPress Enable two-factor authentication on WordPress: authenticator app or email codes, which roles must enroll, grace period, and how to recover a lost phone.
- WordPress core files were modified: what it means A core-file warning means a checksum mismatch, not an automatic hack. How to read the diff, when it is harmless, and when to restore or treat it as malware.
- When a security plugin is enough vs when to hire cleanup A plugin is the weekly stack you run yourself. Hired cleanup is humans for a live compromise or a written review. How to buy the right job, not a second dashboard.
- WordPress Security Monitoring: What It Actually Means WordPress security monitoring explained: plugin schedules, events logs, external uptime checks, and human retainers. What each covers and what none of them replace.
- wp2shell: Critical WordPress core vulnerability actively exploited wp2shell (CVE-2026-63030, CVE-2026-60137): confirm 6.8.6, 6.9.5, or 7.0.2. Check leftover admins such as [email protected] and wp2shell.local.
Artículos en inglés
Firewalls y escáneres
Compara firewalls, escáneres y cómo funciona de verdad la protección por capas.
- Security Ninja vs MalCare 2026 Fair Security Ninja vs MalCare comparison for 2026: in-dashboard all-in-one toolkit versus cleanup-oriented malware workflows, and when each fits.
- Security Ninja vs Patchstack 2026 Fair Security Ninja vs Patchstack comparison for 2026: in-dashboard all-in-one toolkit versus virtual patching for known vulnerabilities, and when to use each.
- WordPress WAF: Plugin Firewall vs Cloud WordPress WAF compared: plugin firewall vs cloud or edge WAF. Where each runs, what each blocks, when to use both, and why stacking three firewalls backfires.
- Ninja Firewall vs Security Ninja (Not the Same Plugin) Ninja Firewall is NinTechNet, not WP Security Ninja. Same ninja word, different companies. Firewall-only tool vs a Free-to-Pro stack.
- Security Ninja vs Solid Security 2026 Security Ninja vs Solid Security (formerly iThemes) in 2026: hardening-first vs an all-in-one Free-to-Pro WordPress security stack.
Artículos en inglés
WooCommerce y ecommerce
Asegura tiendas, protege datos de clientes y mantén el checkout de confianza.
- WooCommerce Checkout and Coupon Security Secure WooCommerce checkout and coupons: bot abuse, credential stuffing, skimming risk, rate limits, and staff access. Satellite guide to the WooCommerce security hub.
- WooCommerce abuse: fake checkouts, coupon attacks, and rate limits Coupon guessing and checkout hammering drain stores without a classic “hack.” Signals to watch and a tuning-first rate-limit approach that protects real shoppers.
- WordPress ecommerce vs WooCommerce: what's the difference WordPress ecommerce usually means WooCommerce: WordPress is the CMS, WooCommerce is the store plugin. Honest tradeoffs vs hosted carts, then the security work that comes with ownership.
- WooCommerce Protected Categories: password and role gates Set up WooCommerce Protected Categories (Barn2) with passwords, roles, or users. Test add to cart, cache pitfalls, and store hardening that still matters.
- Secure WordPress Forms: Practical Tips That Stick Secure WordPress contact and upload forms: spam vs exploit threats, CAPTCHA choices, file uploads, plugin vetting, rate limits, and safe storage without hack-proof claims.

Artículos en inglés
Copias de seguridad y recuperación
Cómo planear copias y restauraciones con tu hosting o un plugin de backup, y qué hacer cuando algo falla.
- WordPress Backup Security Plugins 2026 How to choose WordPress backup plugins vs security plugins: what each job covers, how to keep backups safe, and where Security Ninja fits.
- Recover WordPress SEO After a Hack Recover WordPress SEO after a hack: Japanese keyword spam, Search Console Security Issues and Manual Actions, sitemap cleanup, and reconsideration requests.
- WordPress care plan: what security maintenance should include WordPress security maintenance care plan checklist: updates, malware scans, vulnerability monitoring, backups, login hygiene, and clear cleanup terms. How it differs from a plugin license.
- WordPress backup best practices: offsite copies and tested restores How to back up WordPress properly: files plus database, automatic jobs, offsite storage, retention, encryption where it helps, and proving a restore works.
- Website Backup Plan: Survive a Site Compromise & Recover Fast Build a simple WordPress backup and recovery plan: clean backups, early alerts, restore steps, and what to do if malware or a hack takes the site down.
Artículos en inglés
Guías para principiantes
Empieza aquí si eres nuevo en seguridad WordPress o necesitas la visión general.
- Do I need a WordPress security plugin? Honest answer: you can harden WordPress without a plugin, but most sites still benefit from one stack for scans, vulns, login, and firewall. Free vs Pro jobs explained.
- Do security plugins slow down WordPress? Yes, some can, usually from heavy on-server scans, live logging, or stacked firewalls. How architecture and settings matter, and what Security Ninja does differently.
- WordPress Security for Beginners 2026: Easy Protection Guide WordPress security for beginners: simple steps for updates, logins, plugins, backups, scanning, and what to do if something looks wrong.
- WordPress Security Configuration Guide 2026 Configure WordPress security without fluff: wp-config, users, host settings, plugin module order, staging vs production, and links to deeper hardening guides.
- WordPress Security Plugin Setup Guide 2026 Set up a WordPress security plugin the sensible way: Free baseline first, then Pro firewall, malware, and login hardening. Includes stacking rules, false positives, and agency tips.

Artículos en inglés
Todos los artículos
Página 1 de 7 · en inglés
- How to enable 2FA on WordPress Enable two-factor authentication on WordPress: authenticator app or email codes, which roles must enroll, grace period, and how to recover a lost phone.
- WordPress core files were modified: what it means A core-file warning means a checksum mismatch, not an automatic hack. How to read the diff, when it is harmless, and when to restore or treat it as malware.
- When a security plugin is enough vs when to hire cleanup A plugin is the weekly stack you run yourself. Hired cleanup is humans for a live compromise or a written review. How to buy the right job, not a second dashboard.
- Security Ninja vs MalCare 2026 Fair Security Ninja vs MalCare comparison for 2026: in-dashboard all-in-one toolkit versus cleanup-oriented malware workflows, and when each fits.
- Security Ninja vs Patchstack 2026 Fair Security Ninja vs Patchstack comparison for 2026: in-dashboard all-in-one toolkit versus virtual patching for known vulnerabilities, and when to use each.
- WooCommerce Checkout and Coupon Security Secure WooCommerce checkout and coupons: bot abuse, credential stuffing, skimming risk, rate limits, and staff access. Satellite guide to the WooCommerce security hub.
- WordPress Malware Cleanup: DIY or Hire Help? After you confirm a WordPress hack: when to clean malware yourself, when to hire cleanup, what a good incident response includes, and how to avoid paying twice.
- WordPress WAF: Plugin Firewall vs Cloud WordPress WAF compared: plugin firewall vs cloud or edge WAF. Where each runs, what each blocks, when to use both, and why stacking three firewalls backfires.
- WordPress Security Monitoring: What It Actually Means WordPress security monitoring explained: plugin schedules, events logs, external uptime checks, and human retainers. What each covers and what none of them replace.
- Check if Your WordPress Site Is Hacked Check if a WordPress site is hacked with scans from wp-admin: vulnerabilities, security tests, core integrity, then a logged-out look at users and Search Console.
- Ninja Firewall vs Security Ninja (Not the Same Plugin) Ninja Firewall is NinTechNet, not WP Security Ninja. Same ninja word, different companies. Firewall-only tool vs a Free-to-Pro stack.
- Security Ninja vs Solid Security 2026 Security Ninja vs Solid Security (formerly iThemes) in 2026: hardening-first vs an all-in-one Free-to-Pro WordPress security stack.
- Security Ninja vs Sucuri Security Ninja vs Sucuri: in-dashboard Free-to-Pro toolkit versus a platform WAF and cleanup model, including DNS and proxy ops.
- Security Ninja vs Wordfence Fair Security Ninja vs Wordfence comparison: who each fits, job-by-job coverage, and when one stack is the better pick.
- Do I need a WordPress security plugin? Honest answer: you can harden WordPress without a plugin, but most sites still benefit from one stack for scans, vulns, login, and firewall. Free vs Pro jobs explained.
- Do security plugins slow down WordPress? Yes, some can, usually from heavy on-server scans, live logging, or stacked firewalls. How architecture and settings matter, and what Security Ninja does differently.
- wp2shell: Critical WordPress core vulnerability actively exploited wp2shell (CVE-2026-63030, CVE-2026-60137): confirm 6.8.6, 6.9.5, or 7.0.2. Check leftover admins such as [email protected] and wp2shell.local.
- An unknown WordPress admin: the calm response that keeps the incident short A client spotted an unrecognized administrator named wpmaint. How we contained access, checked plugins and themes, and left the site more disciplined than before.
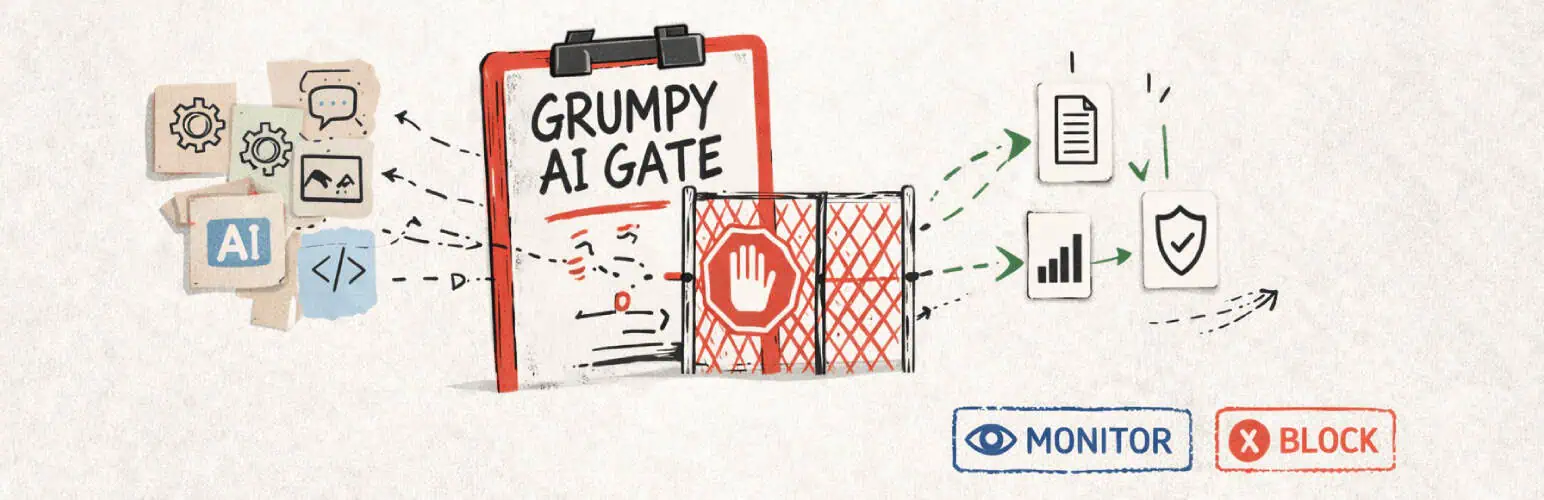
- Monitor WordPress AI plugin activity with Grumpy AI Gate Grumpy AI Gate shows which WordPress plugins talk to AI providers, logs usage locally, and can block selected WordPress AI Client flows.
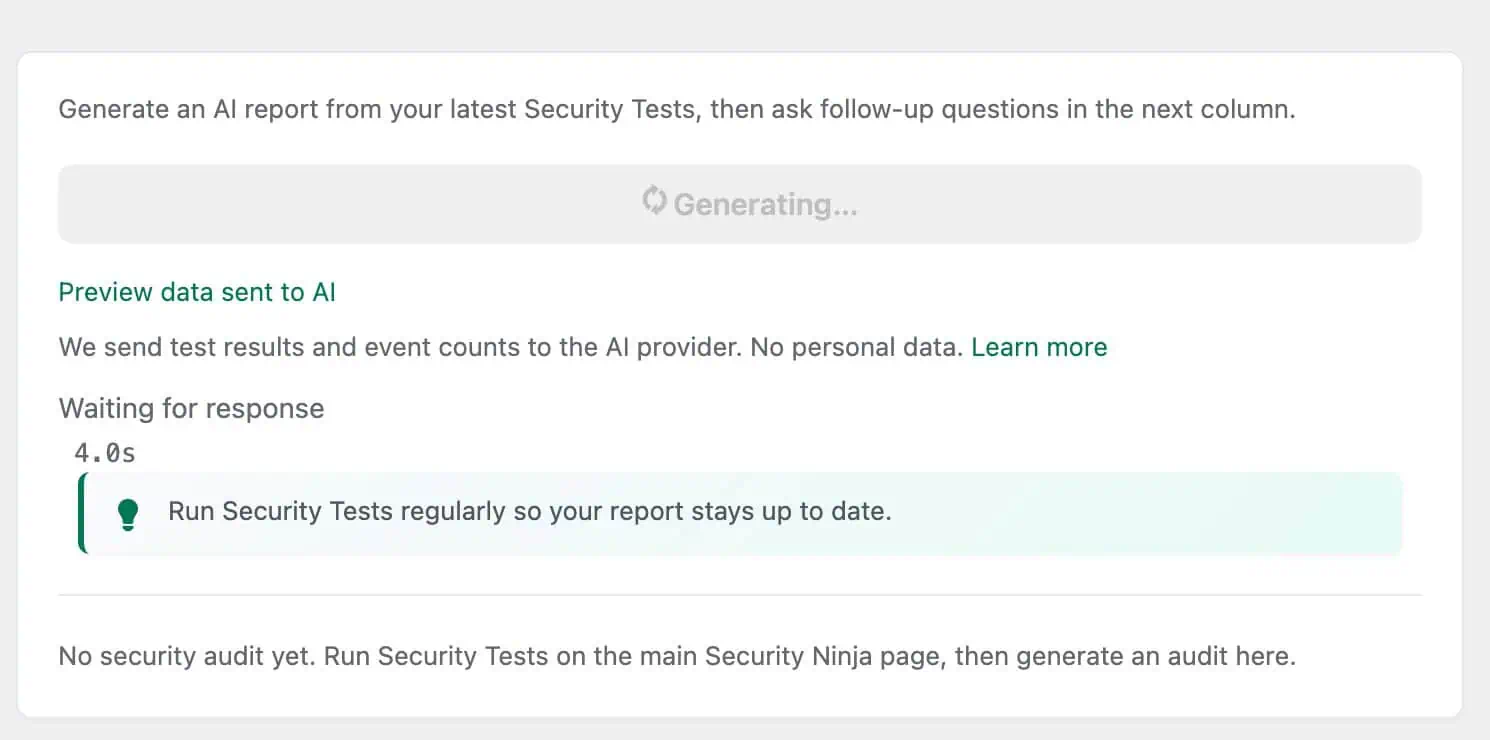
- Why we built the AI Security Advisor How WP Security Ninja’s AI Security Advisor turns real scan data into plain-language next steps on WordPress 7, without inventing another chatbot.
¿Listo para proteger tu sitio WordPress?
WP Security Ninja combina pruebas de seguridad, escaneo de malware, firewall y protección de acceso en un solo plugin.
