Blog / Page 2
All articles
Page 2 of 7
- wp2shell: Critical WordPress core vulnerability actively exploited WordPress 7.1.2 is a critical core security release (CVE-2026-87902). 7.1.1 patched Click2Shell and Comment2Shell. July leftover-access checks still apply.
- An unknown WordPress admin: the calm response that keeps the incident short A client spotted an unrecognized administrator named wpmaint. How we contained access, checked plugins and themes, and left the site more disciplined than before.
- Monitor WordPress AI plugin activity with Grumpy AI Gate Grumpy AI Gate shows which WordPress plugins talk to AI providers, logs usage locally, and can block selected WordPress AI Client flows.
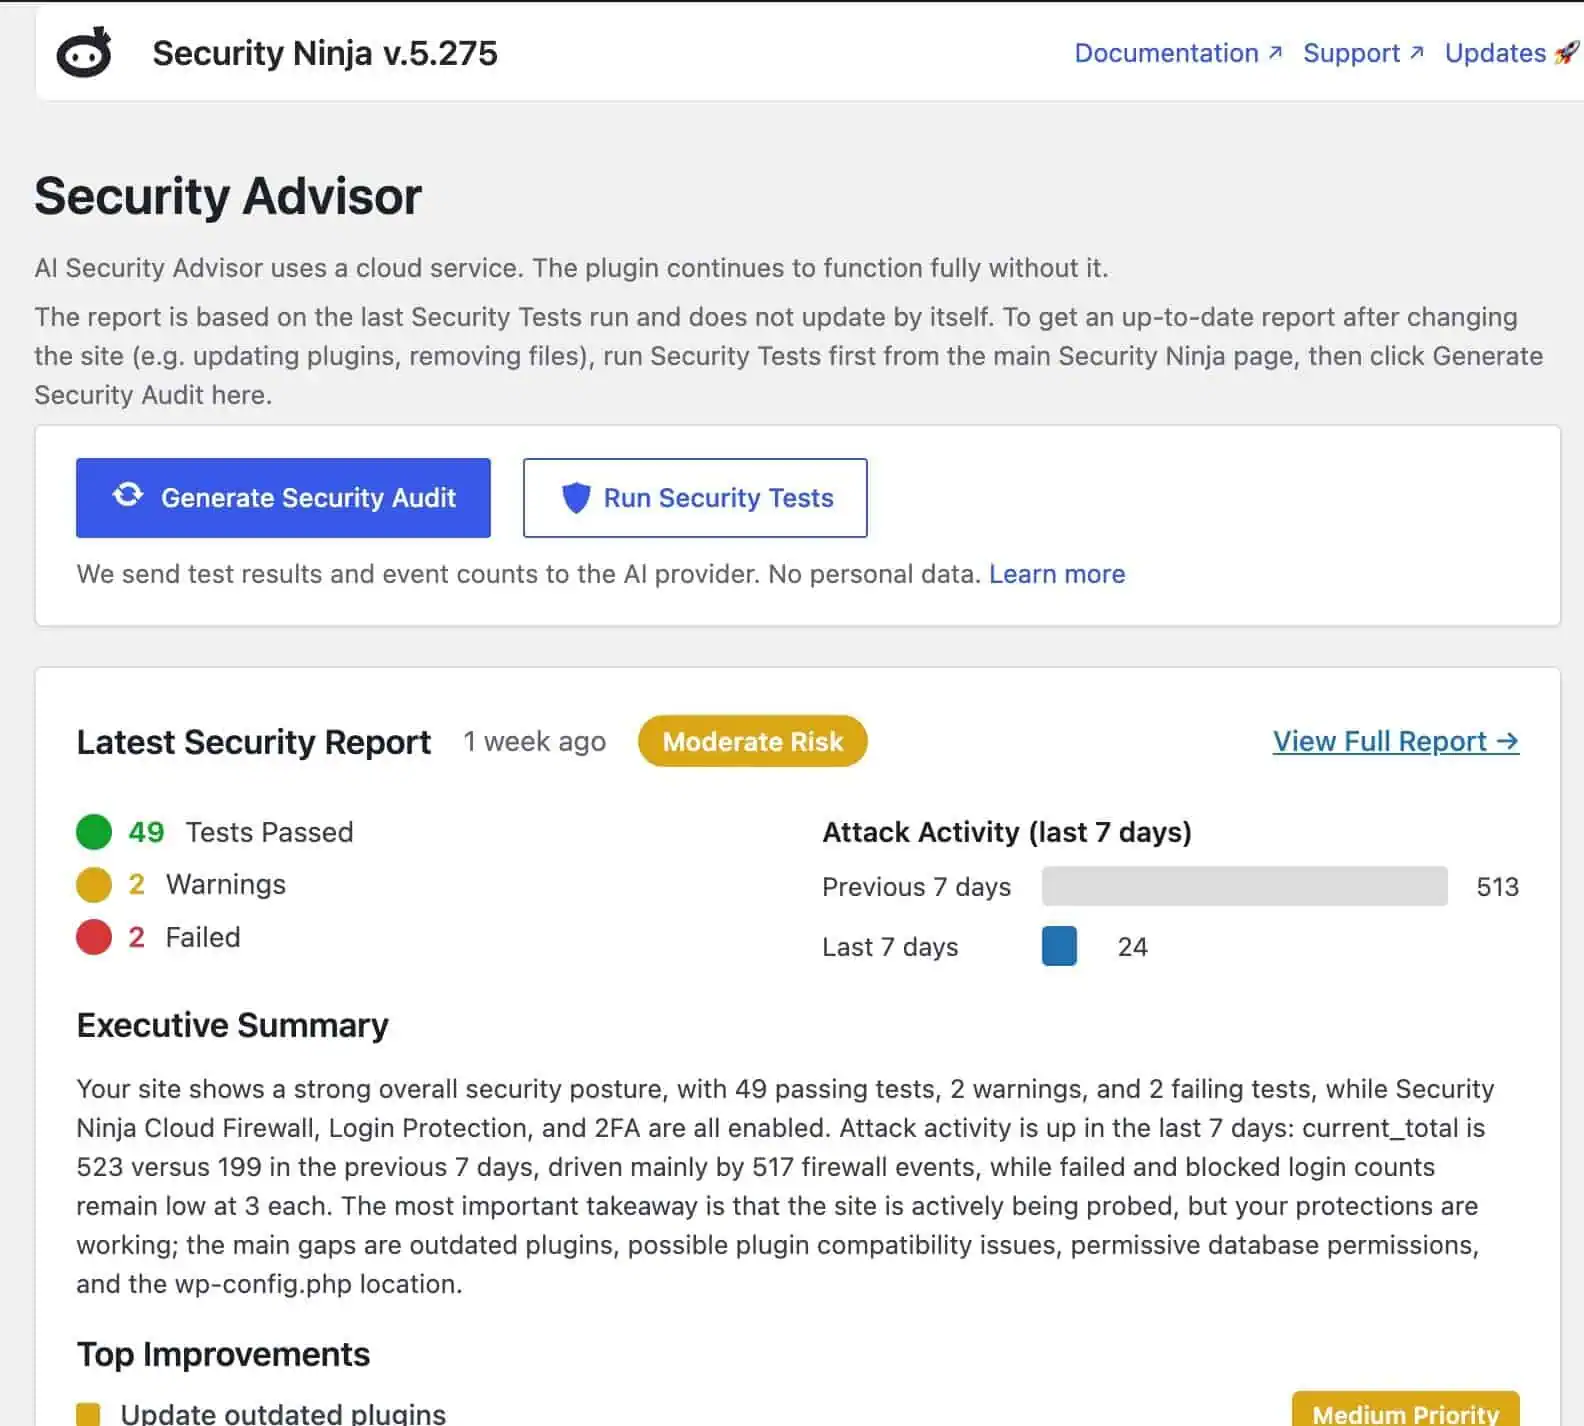
- Why we built the AI Security Advisor How WP Security Ninja’s AI Security Advisor turns real scan data into plain-language next steps on WordPress 7, without inventing another chatbot.
- WP Security Ninja and WordPress 7 AI connectors How the AI Security Advisor uses WordPress 7 AI connectors to turn real Security Ninja scan data into plain-language reports, on Free and Pro.
- Recommended tools for WordPress professionals A short, honest list of tools we use or trust for WordPress hosting, workflows, GraphQL, resets, and growth. No paid placements dressed up as advice.
- WordPress security patterns we keep seeing (and simple fixes) Recurring WordPress security problems: postponed updates, messy access, no logs, untested backups, bot noise, and one-time security installs. Plus a simple baseline.
- Why 404s can spike your hosting bill (and how to calm bot noise) 404 hammering burns CPU even when pages do not exist. Confirm the pattern in logs, then cut junk earlier with firewall and rate limits.
- WooCommerce abuse: fake checkouts, coupon attacks, and rate limits Coupon guessing and checkout hammering drain stores without a classic “hack.” Signals to watch and a tuning-first rate-limit approach that protects real shoppers.
- WordPress hacked after a developer handoff: the leftover file problem A leftover developer file manager acted as a WordPress backdoor. How to find it, clean up, and stop permanent “helpful” access tools.
- The malware that kept coming back: the cron job we finally found A WordPress site was cleaned twice, but redirects returned. The root cause was a hosting cron job reinjecting malware on a schedule.
- WordPress security for beginners WordPress security for beginners: simple steps for updates, logins, plugins, backups, scanning, and what to do if something looks wrong.
- WordPress security configuration Configure WordPress security without fluff: wp-config, users, host settings, plugin module order, staging vs production, and links to deeper hardening guides.
- WordPress security plugin conflicts How to spot and fix WordPress security plugin conflicts: overlapping firewalls, login hardeners, and scanners that fight each other.
- WordPress backup and security plugins How to choose WordPress backup plugins vs security plugins: what each job covers, how to keep backups safe, and where Security Ninja fits.
- How to set up a WordPress security plugin Set up one WordPress security plugin: Free tests first, then firewall, malware, and login. Do not stack two suites.
- WordPress security audit A practical WordPress security audit: what to check, which tools to run, how to prioritize fixes, and when to get help.
- How to secure a WordPress login How to secure a WordPress login: unique passwords, 2FA for admins, failed-login limits, and fewer administrators.
- WordPress security checklist A printable WordPress security checklist: HTTPS, updates, passwords/2FA, backups, WAF/scans, least privilege, admin hardening, remove unused, and monitoring.
- WordPress firewall plugins A WordPress firewall plugin filters bad HTTP before it hits wp-admin. Plugin vs cloud WAF, what it actually blocks, and how to pick one without stacking tools.