On Pro, the Installation Wizard can apply a recommended set of Fixes in one step. You can change any of these later under Security Ninja → Fixes.
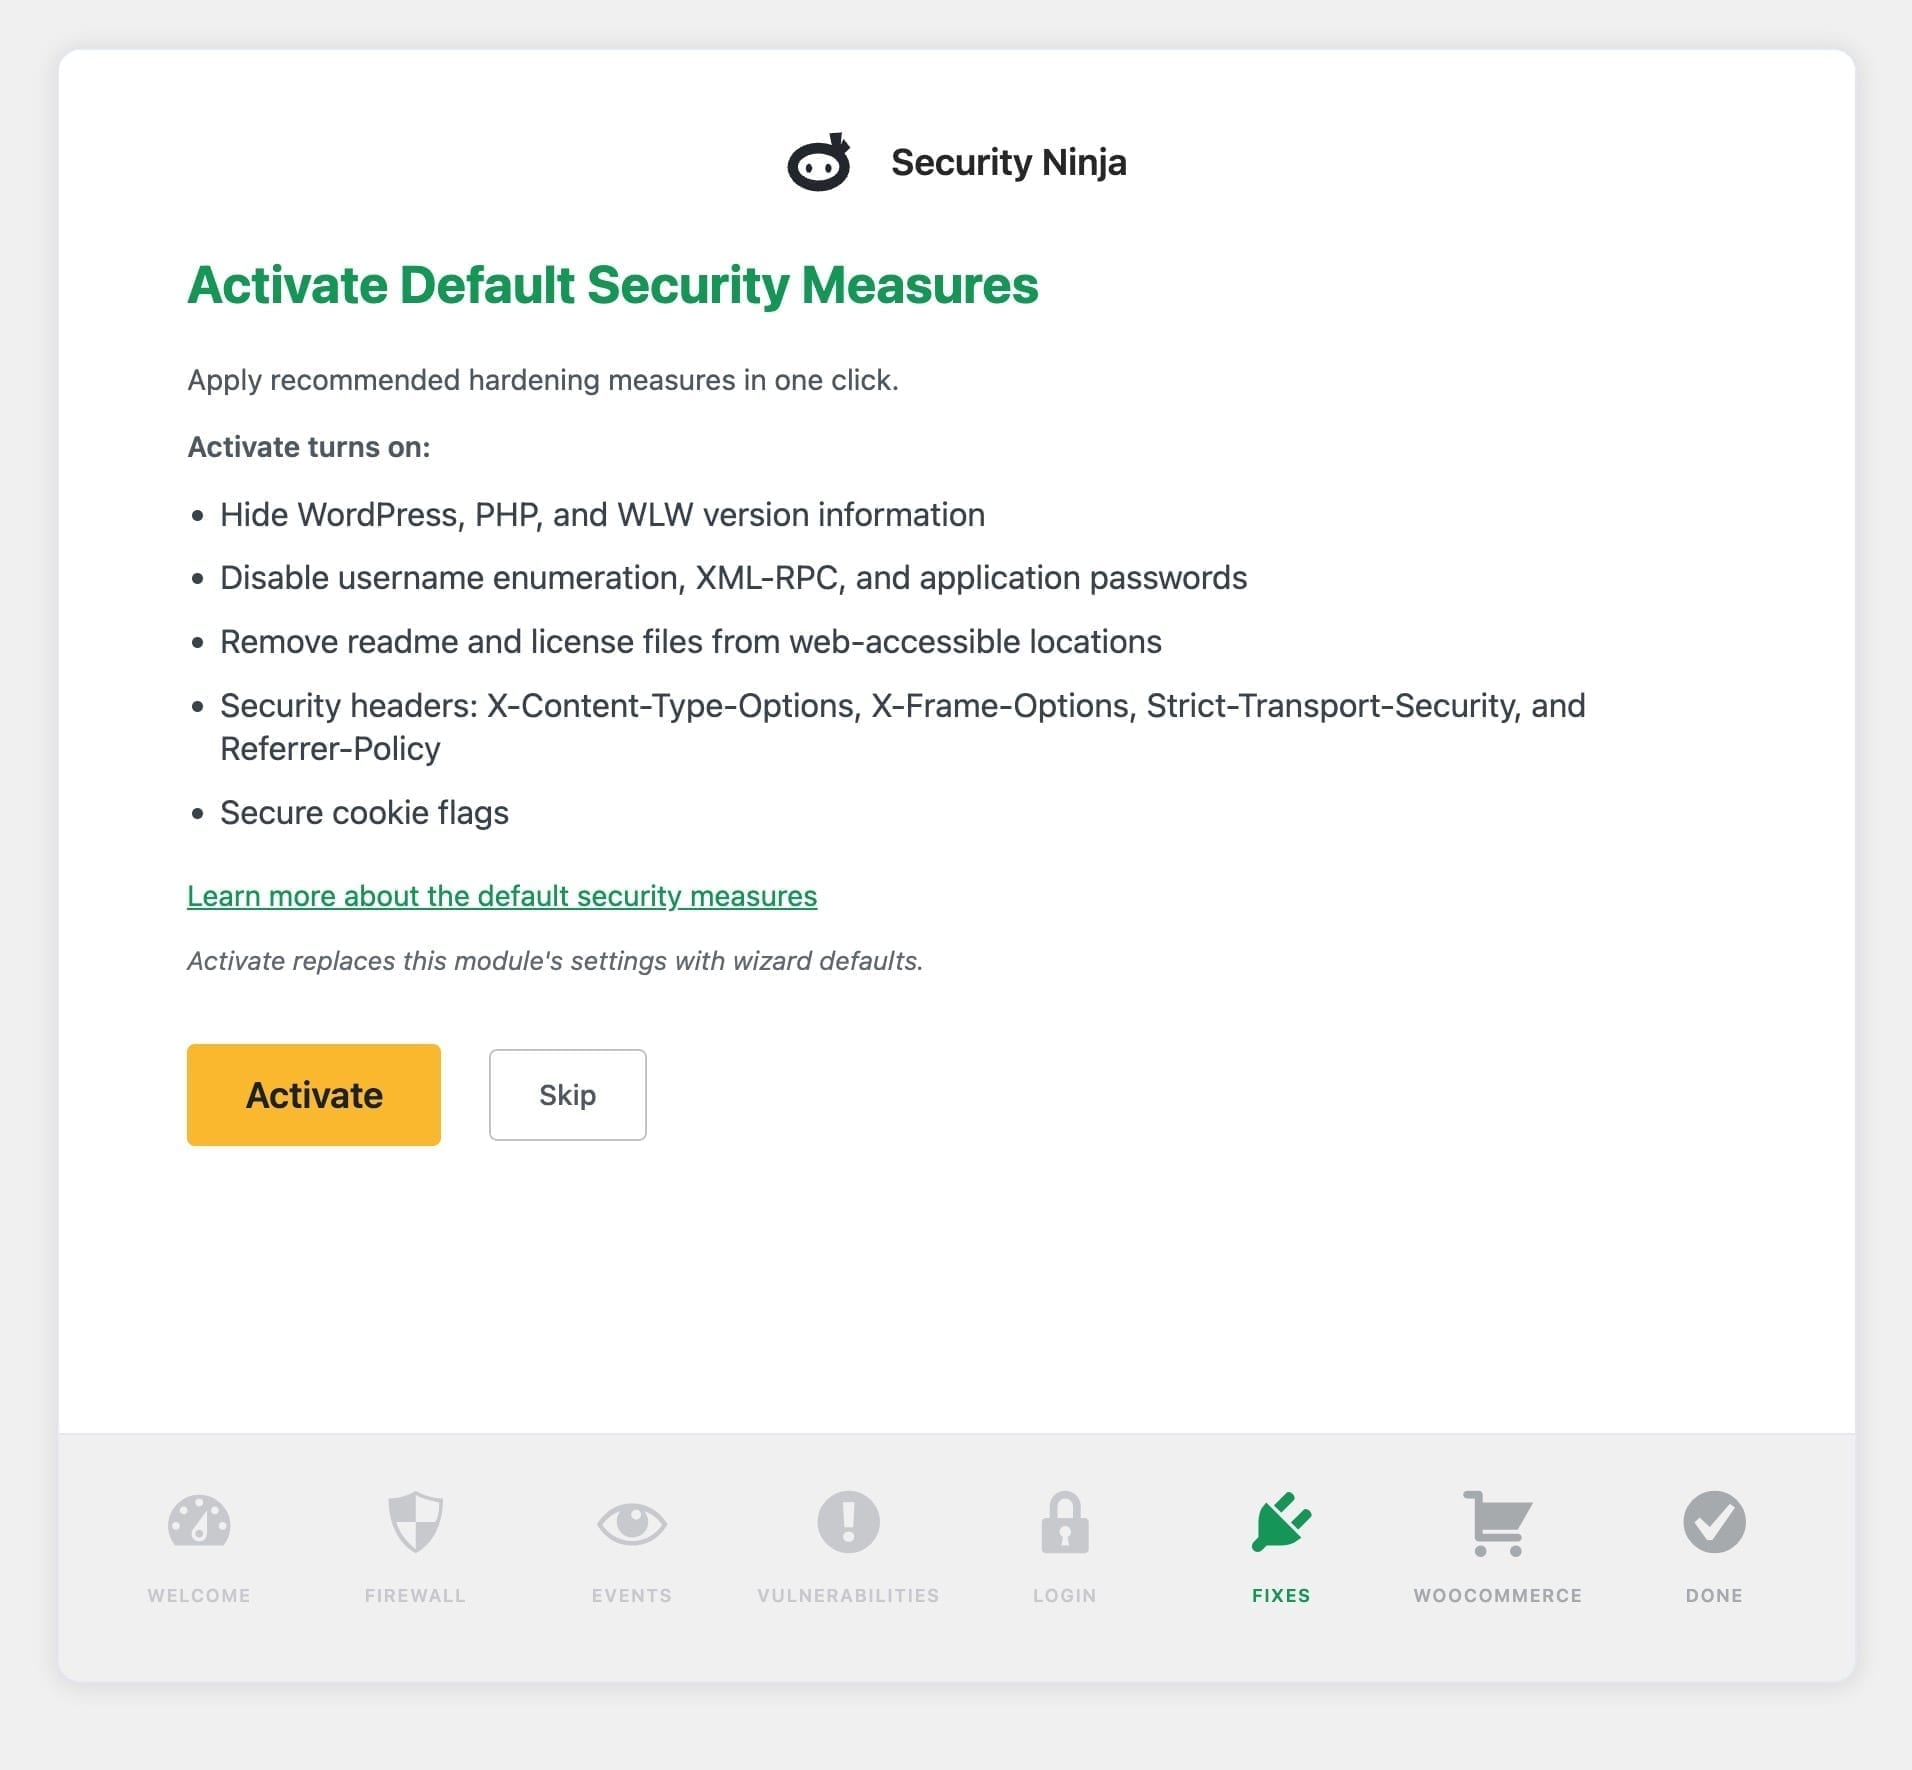
What Activate turns on
- Hide WordPress Generator tag
- Removes the WordPress version from HTML so attackers cannot target a known release as easily.
- Hide Windows Live Writer tag
- Removes an unused meta tag from the HTML head.
- Hide PHP version in headers (removes X-Powered-By)
- Stops the server from advertising the PHP version in HTTP headers when the plugin can control that output.
- Hide WP Debug
- Turns off debug output that can leak site details to visitors.
- Disable username enumeration
- Blocks common tricks that reveal valid usernames.
- Disable XML-RPC
- Turns off XML-RPC, which is a frequent brute-force and abuse target if you do not need it.
- Disable application passwords
- Turns off WordPress application passwords as an alternate login method.
- Remove unneeded files
- Removes leftover readme and license files from web-accessible plugin and theme locations when the fix can do so safely.
- Enable secure cookies
- Marks cookies secure so they are only sent over HTTPS.
- Enable default security headers
- Adds X-Content-Type-Options, X-Frame-Options, Strict-Transport-Security, and Referrer-Policy with sensible defaults.
These options are Pro Fixes. Free users finish the wizard without this step. Review the list after Activate if your site needs XML-RPC, application passwords, or different header values.
