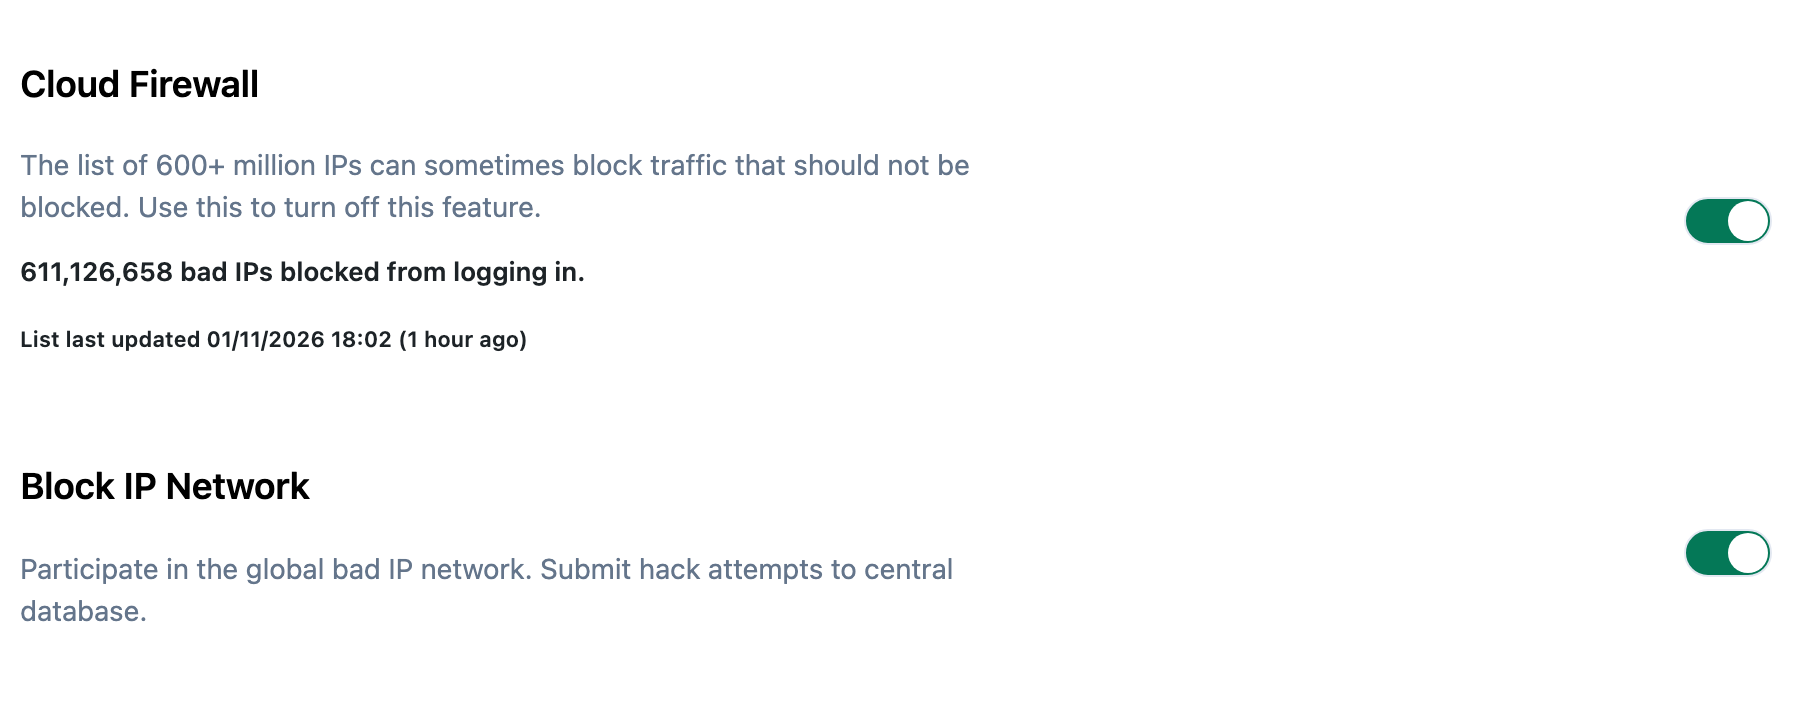
Block IP Network (Pro) is the shared list of attack IPs reported by participating Security Ninja sites. When it is on, your site can submit blocked attack traffic and download that shared list, so other sites can block those IPs earlier.
It is not the same switch as Cloud Firewall, which is the large public bad-IP list (600M+ addresses). Both live on Security Ninja → Firewall → Settings. You can use one, the other, or both.
Free vs Pro
- Free: 8G-based request firewall that blocks many malicious request patterns. It does not join Block IP Network.
- Pro: Block IP Network, plus the separate Cloud Firewall list (600M+ known bad IPs), login protection, country blocking, rename login, and 2FA. See How to use the firewall.
What gets shared
Reports go to api.wpsecurityninja.com. They are queued on your site and sent in batches: about every 15 minutes, or sooner once 25 unique IPs are waiting. Each report is the blocked IP, a short reason, a block type, a hit count, and the license and install ids needed to accept the report.
The shared list is downloaded once a day. Entries older than 24 hours are dropped locally on that refresh.
These matches stay on your site and are not sent:
- User-agent blocks
- Referrer blocks
- Hostname (blocked host) matches
Repeated failed logins are reported as failed logins. Blocks that Early Firewall catches before WordPress loads are reported when WordPress imports them, with the same exceptions above.
WooCommerce and SureCart payment and webhook requests skip some of these reports so a gateway token is not filed as an attack. See store protection.
Cloud Firewall list (separate)
Cloud Firewall downloads a public set of addresses tied to spam, malware, and attacks: FireHOL Level 1. That download runs daily in the background (secnin_update_cloud_firewall). It does not read email, and it is not the Block IP Network list.
Country blocking and this cloud list can be softened for satellite ISPs such as Starlink. Manual blocks and suspicious-request filtering are not. See How to block a country.
Privacy
Data sent for Block IP Network is limited to what the shared list needs: the blocked IP, the site reporting it, and the reason. It is not used to build a profile of ordinary visitors. User-agent strings from those blocks are not uploaded.
More detail: non-sensitive diagnostic data, privacy policy, and GDPR.