WordPress can expose usernames in two common ways:
?author=Nscans that redirect to/author/username/when the ID exists.- Anonymous REST requests to
/wp-json/wp/v2/users(or?rest_route=/wp/v2/users) that list users without logging in.
Attackers use those paths to collect valid usernames before password guessing. Disabling username enumeration makes that harder.
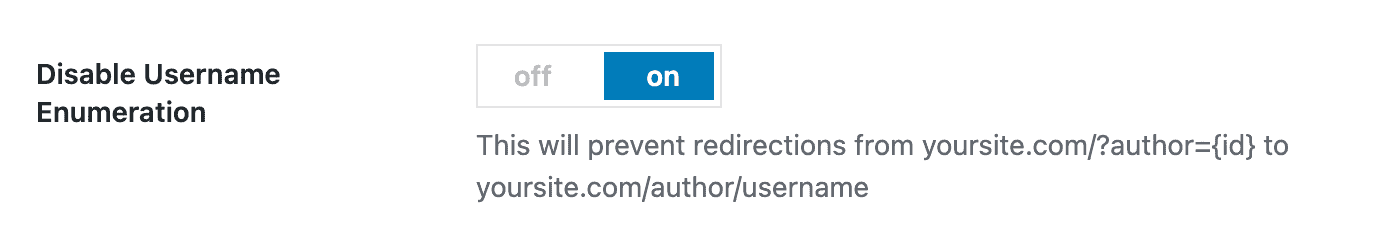
Enable in Security Ninja
- Go to Security Ninja → Fixes.
- Turn on Disable Username Enumeration.
- Save.
This Fix (Pro) does the following:
- Blocks classic
?author=Nenumeration attempts. It matches the WordPressauthor=query parameter only, not unrelated parameters such asbook_author=. - Skips the block for logged-in users so normal admin workflows keep working.
- Removes anonymous access to the REST users endpoint (
/wp-json/wp/v2/usersand the?rest_route=form). - Filters oEmbed author data where applicable.
Security Tests include a check for REST user listing on that path.
Optional server-level hardening
You can also block author archive probes in .htaccess if you prefer a server rule:
# Block access to author scans
RewriteEngine On
RewriteCond %{QUERY_STRING} ^author=([0-9]*) [NC]
RewriteRule ^ - [F,L]
The Security Ninja Fix is usually enough on its own. Use server rules only if you need an extra layer.
Related practices
- Avoid predictable usernames like
admin. - Use login form protection and 2FA on Pro sites.
- Run Security Tests after enabling the Fix to confirm the REST check passes.
