The vulnerability scanner checks whether known vulnerabilities affect your WordPress core, themes, or plugins.
Go to Security Ninja → Vulnerabilities.
When a vulnerability is detected
A warning notice shows how many issues were found. You can open the finding, go to the plugin page, or dismiss the notice.
A dismissed warning stays hidden for 24 hours. It returns unless you update or remove the vulnerable software.
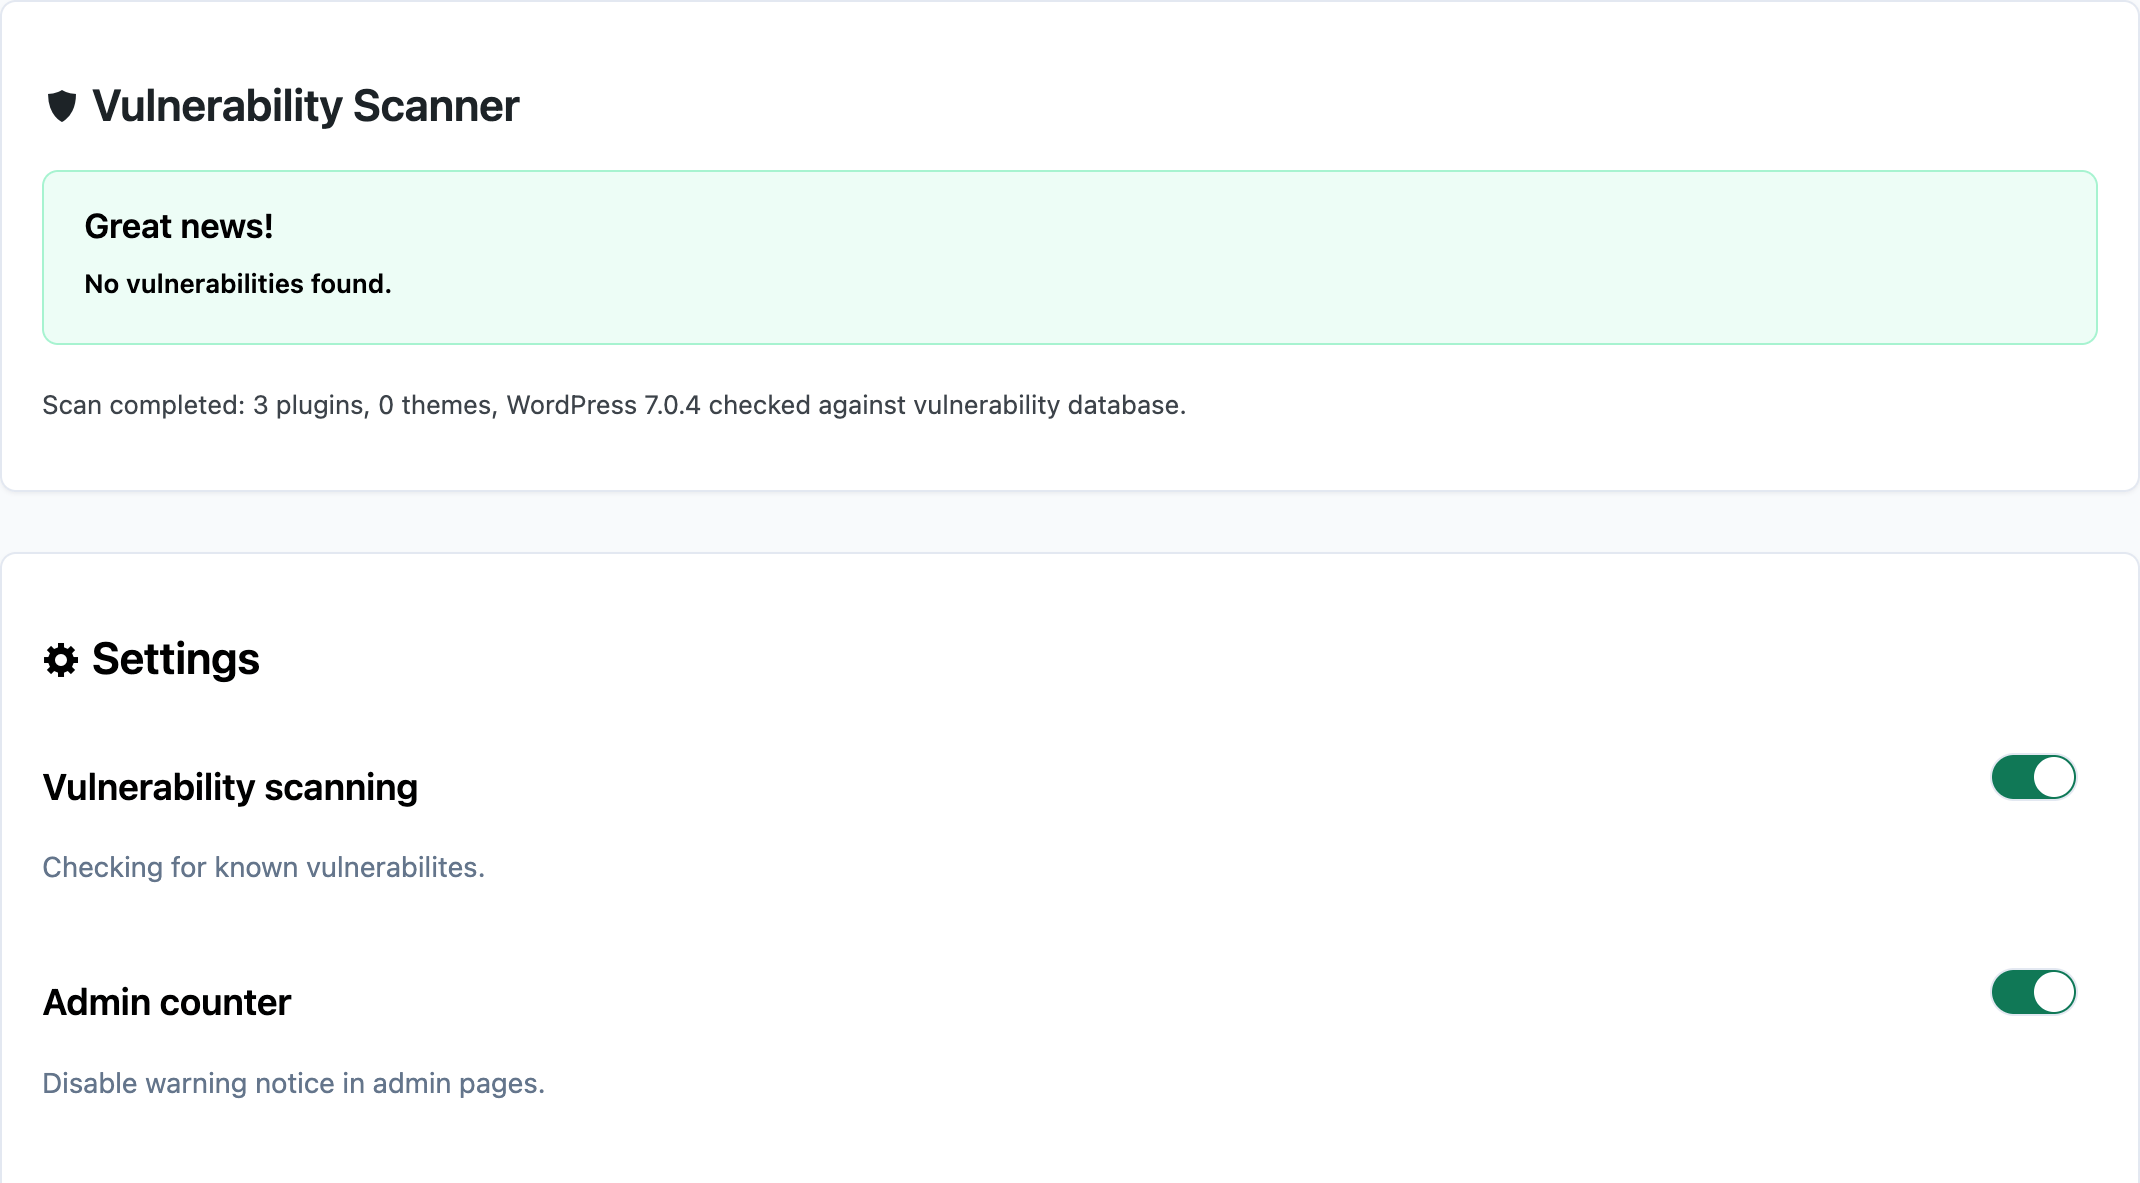
The vulnerability list
The list is downloaded from the Security Ninja API and refreshed on a schedule (including background updates). At the bottom of the Vulnerabilities tab you can see how many known vulnerabilities are in the list and when it was last updated.
Settings
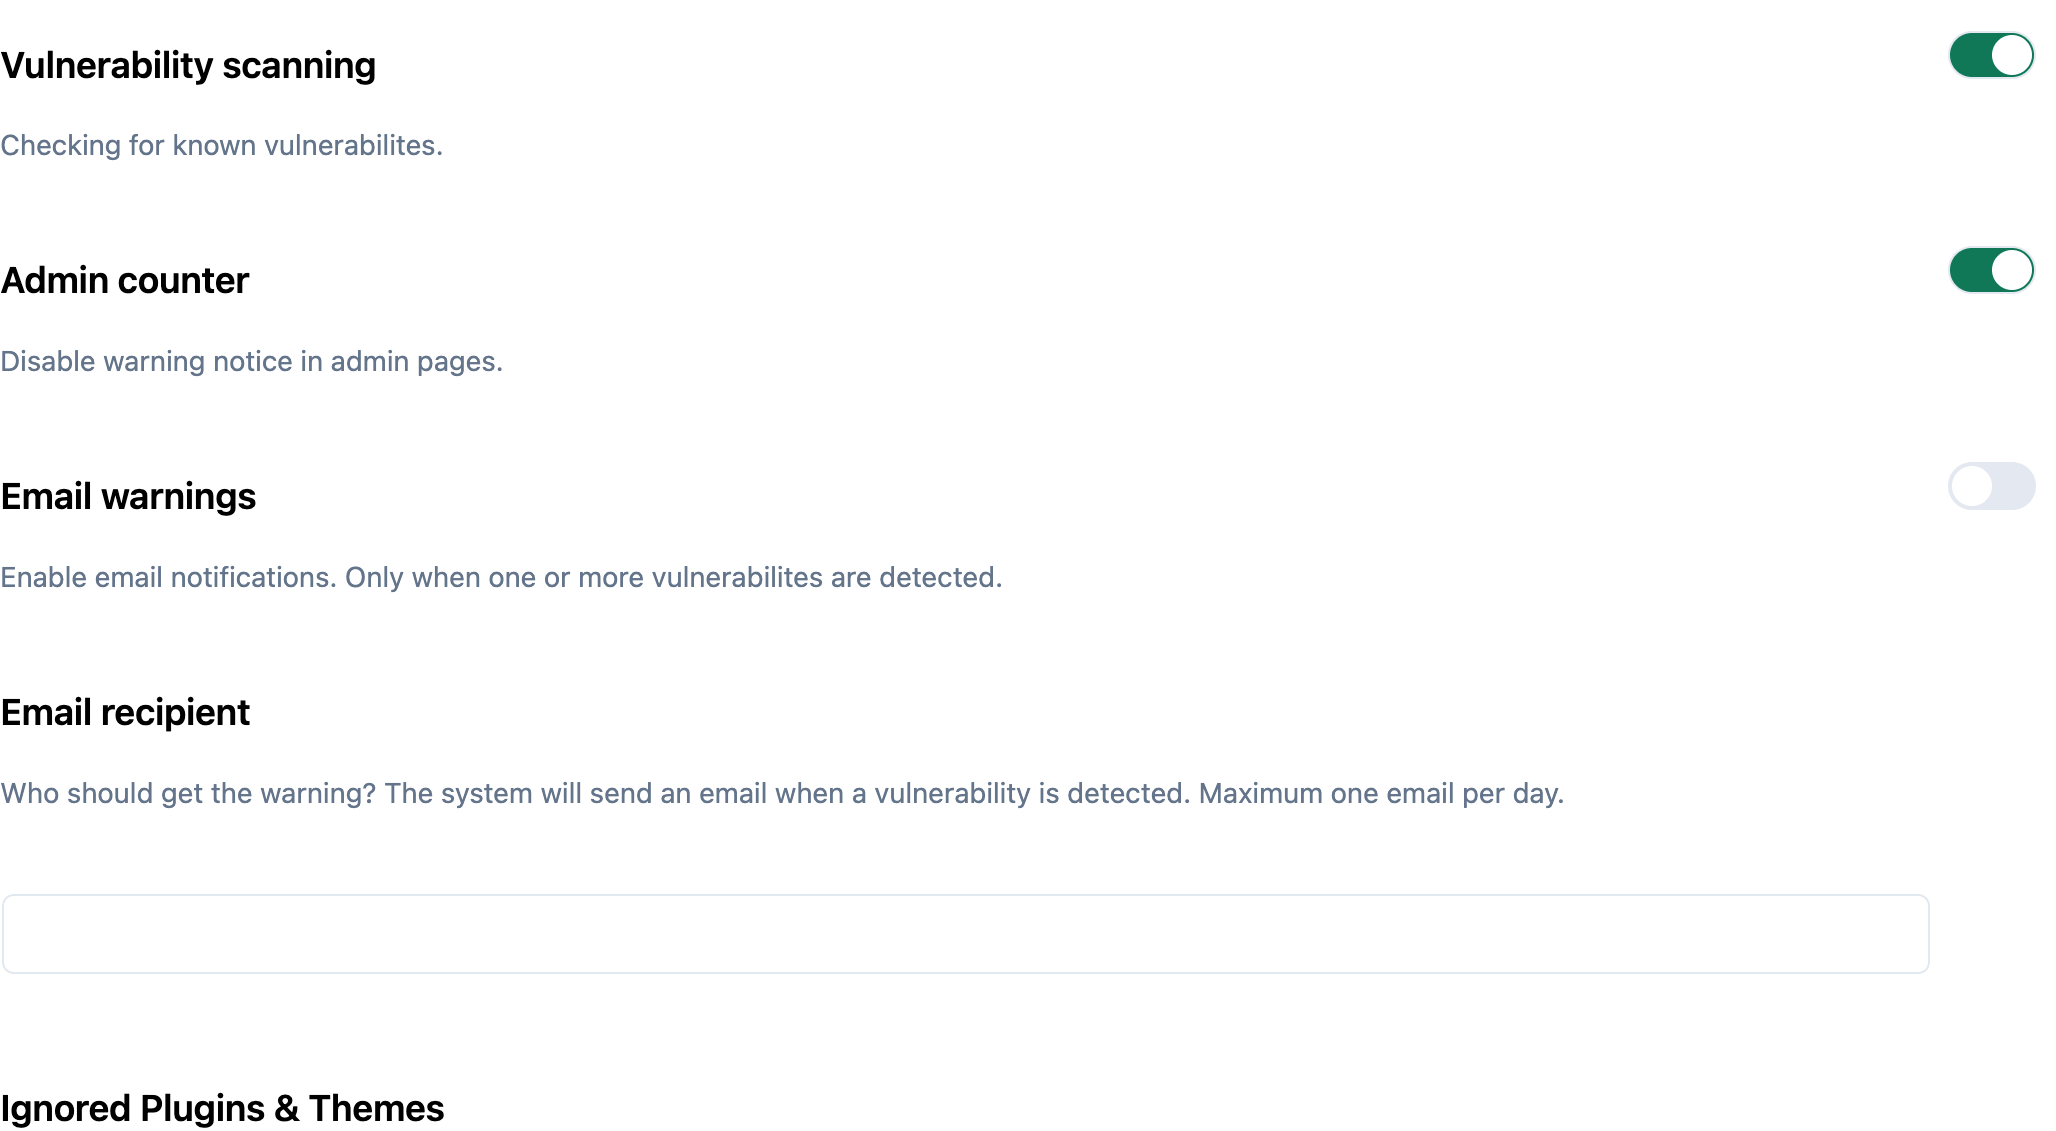
Vulnerability scanning
Turn the scanner on or off. Keep it enabled unless you have a clear reason not to.
Admin counter
When vulnerabilities are found, a small counter can appear next to the Security Ninja menu item and inside the plugin UI. Use this setting to control that badge.
Email warnings
If you do not log in every day, enable email warnings and set a recipient so you do not miss new findings.
Email recipient
Enter who should receive warnings. The same set of findings is not emailed again within 24 hours. A new distinct set of CVEs can trigger another email the same day. Scheduled emails wait for a finished scan and skip plugins or themes that are gone or already patched.
Details: Email alerts for detected vulnerabilities.
Ignored plugins and themes
Enter plugin or theme folder names, one per line, to skip during vulnerability scanning. Those items are ignored even if a known vulnerability matches. Example: designthemes-core-features or twentytwentyfour.
Click Save Changes after you edit settings.
The vulnerability scanner is free for all Security Ninja users and remains free.
